Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Trustwave MailMarshal Email Security Protects Against WinRAR Vulnerability CVE-2023-38831

The importance of email security cannot be understated. Proof of this can be seen in some recent research conducted by the Trustwave SpiderLabs team around our email security product MailMarshal. The team recently ran an experiment on known Zero Day CVE-2023-38831 found in RARLabs WinRAR that is currently being exploited in the wild in WinRAR versions 6.23 and earlier. WinRAR is a compression, archiving, and archive managing software tool.
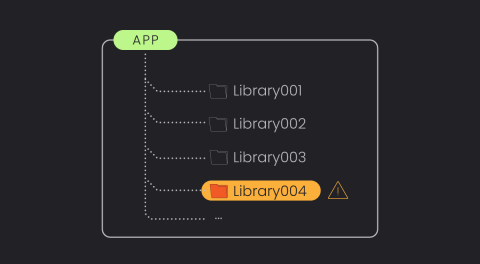
The Power of Library-Based Vulnerability Detection.

With an ever-growing number of vulnerabilities being discovered annually, vulnerability management tools are rapidly evolving to handle and prioritize these risks. However, it remains one of the most overwhelming and time-consuming areas in cybersecurity. There’s still significant room for enhancement, especially in reducing false alerts and prioritizing genuine threats.

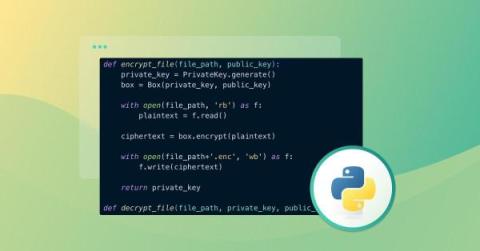
File encryption in Python: An in-depth exploration of symmetric and asymmetric techniques

In our modern world, we constantly share private, confidential, and sensitive information over digital channels. A fundamental component of this communication is file encryption — transforming data into an unreadable format using encryption algorithms.

Citrix Bleed Vulnerability: SafeBreach Coverage for US-CERT Alert (AA23-325A)

On November 21st, the Cybersecurity and Infrastructure Security Agency (CISA), Federal Bureau of Investigation (FBI), Multi-State Information Sharing & Analysis Center (MS-ISAC), and Australian Signals Directorate’s Australian Cyber Security Center (ASD’s ACSC) released an advisory highlighting the ongoing exploit of the Citrix Bleed Vulnerability (CVE-2023-4966) by Lockbit 3.0 affiliates.

Vulnerability Management Needs Threat Intelligence: Here's How To Combine Them

In 2022, more than 25,000 new CVEs were discovered and added to the NIST National Vulnerability Database. In just the first ten months of 2023, another 23,500 CVEs were identified and added to the NIST NVD. That’s more than 48,000 new vulnerabilities documented in less than 2 years! With so many new CVEs being identified all the time, vulnerability management can seem like an insurmountable challenge. Despite the staggering numbers, there’s good news.

Digital Supply-Chain Attacks: Exploits and Statistics

Growing digital connectivity has led to the rise of digital supply-chain attacks. This session will explain, demonstrate, and provide statistics about the complexity of the problem and about attacks that arose due to dependencies on external infrastructures. While there is no simple solution to the problem, we will present a strategy to reduce exposure and create processes to avoid such vulnerabilities.