For the past 12 years in Austin, TX, the last week of October has been reserved for the Lonestar Application Security Conference (LASCON). Unequivocally, LASCON is the best cybersecurity conference you have never heard of! LASCON is the annual confab of the Austin, TX OWASP (the Open Worldwide Application Security Project) chapter. OWASP is a volunteer organization that is a treasure trove of application security information with things such as standards, discussion groups, documentation, and more.
We’re proud that Snyk has been honored with inclusion on the inaugural Fortune Cyber 60 list as a top growth-stage company. The full list was unveiled late last week. In 2023, our industry encountered distinctive challenges, but the entire Snyk community demonstrated resilience and a steadfast commitment to our founding mission: empowering and equipping DevSecOps teams worldwide to build securely.
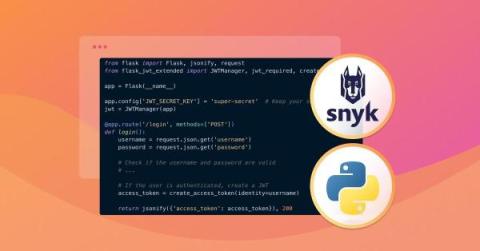
In modern web development, JSON Web Tokens (JWTs) have become a popular method of securely transmitting information between parties. JWTs are used for authentication and authorization and are often used to store user information. However, with the increasing use of JWTs come potential security risks that developers need to be aware of. As a developer, you are responsible for ensuring that your application is secure and user data is protected.
By Vadim Freger, Dolev Moshe Attiya On December 7th, 2023, the Apache Struts project disclosed a critical vulnerability (CVSS score 9.8) in its Struts 2 open-source web framework. The vulnerability resides in the flawed file upload logic and allows attackers to manipulate upload parameters, resulting in arbitrary file upload and code execution under certain conditions. There is no known workaround, and the only solution is to upgrade to the latest versions, the affected versions being.
Apache has released an advisory for a critical vulnerability discovered in Struts versions 2.0.0-2.3.37(EOL), 6.0.0-6.3.0.1 and 2.0.0-2.5.32. This vulnerability is being tracked as CVE-2023-50164 with a CVSS score of 9.8 (Critical) and is reportedly being actively exploited. Impacted versions are affected by a file upload and directory traversal vulnerability that can lead to remote code execution.