Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Latest posts

NSOCKS: Insights into a Million-Dollar Residential Proxy Service

When an adversary wants to target an organization, they want to make it look like they’re coming from a regional or local internet service provider. This makes their activity seem more legitimate and buys time until they get caught. Proxies, which adversaries can use to conceal the origin of malicious traffic, are essential to this process.


Understanding SWIFT CSP: A Comprehensive Introduction to the Framework

SWIFT CSP is a cybersecurity initiative established to ensure that financial institutions adopt strong data control measures to protect their environment against cyberattacks. CSP in Swift stands for Customer Security Programme. However, despite the importance many organizations encounter challenges in interpreting these controls, managing risks posed by third party vendors and aligning outdated systems with SWIFT’s security requirements.

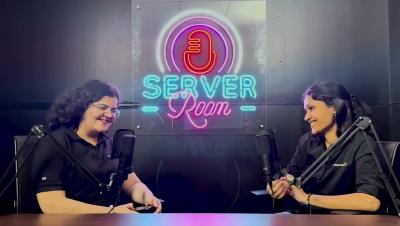
Episode 18: The Alliance Blueprint- How Partnerships Outsmart Cyber Threats ft.Sharada Murthy

In this episode, we invite Sharada Murthy to talk about identity and access management. We talk about the partner channel network and how shared intelligence can be a boon to organisations, password synchronisation vs. password pass through, cybersecurity and a lot more! Tune in right now to listen to the whole conversation!

Challenges for Australian Manufacturers: Insights from the 2025 Trustwave Risk Radar Report

The Trustwave SpiderLabs research 2025 Trustwave Risk Radar Report: Manufacturing Sector takes a global view of the cybersecurity issues facing this vertical, but it’s also important to examine how and if different regions are specifically impacted.