If you're a developer working with Java, you likely know Spring Boot, the robust framework that streamlines the development of stand-alone, production-grade, Spring-based applications. One of the many features it offers is Bean Validation, which is a crucial aspect of any application to ensure data integrity and improve user experience.
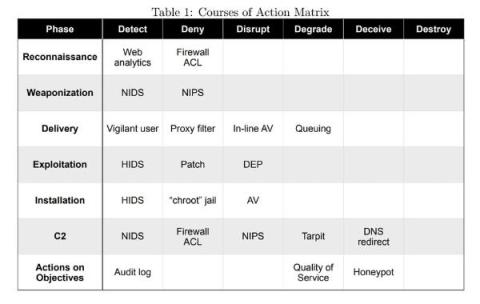
When Eric M. Hutchins, Michael J. Cloppert, and Rohan M. Amin published their paper “Intelligence-Driven Computer Network Defense Informed by Analysis of Adversary Campaigns and Intrusion Kill Chains” in late 2010, they changed the way security personnel thought about defending their digital assets. The paper continues to be a useful model for defense today. This article proposes ways that modern network-derived evidence applies to the kill chain.
With organizations becoming increasingly digitally connected, a lack of visibility into their vendors’ security diligence has made exploiting these relationships a go-to tactic for cybercriminals. Fifty-four percent of publicly reported breaches in the last two years have been due to third parties, vendors, or suppliers, representing one of the greatest cybersecurity risks. Additionally, 98% of organizations have at least one vendor that’s had a breach in the last two years.