Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Security Incident and Event Management.

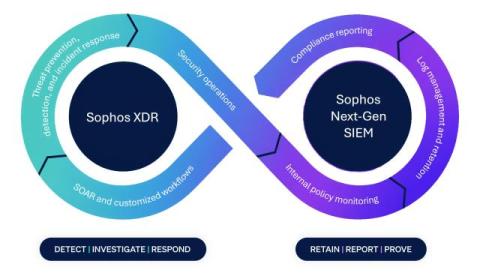
The industry turned XDR and SIEM into categories. Sophos turned them into outcomes.

Sophos Next-Gen SIEM, now generally available as part of Sophos Fusion, brings security operations and compliance together through shared context. For years, the cybersecurity industry has blurred the lines between XDR and SIEM. As capabilities converged, organizations were left trying to connect separate security operations and compliance solutions, often moving the same data between different tools, workflows, and teams.
Tokenpocalypse: Who pays when the AI bill comes due

On this episode of Masters of Data, we dig into what we're calling the tokenpocalypse, the real cost of running AI at the scale most of us have quietly slid into. We trace the whiplash of the past two years, from "everyone needs the AI hammer" to backlash against obvious AI slop, then get into the harder question of what happens when a mission-critical process runs out of tokens, from chaining Claude to Databricks for a custom dashboard to the eye-watering budget Uber reportedly burned through by April.

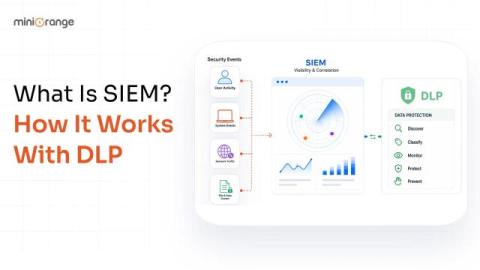
What Is SIEM? How It Works With DLP to Detect Data Threats

Most security teams don’t lose the fight against data breaches because they lack tools. They lose because their tools don’t talk to each other. This is exactly the loophole that SIEM and DLP were built to close, together. Security information and event management gives you visibility into what’s happening across your entire environment. At the same time, data loss prevention gives you the control to stop sensitive information from leaving in the first place.

The security attack that hid inside your observability data

How teams are leaving value on the table and what it costs when they do It's 3:00 a.m. Your on-call engineer gets paged that the central processing unit (CPU) is at 97% on payment-processor-01. They open their observability platform, look at the metric spike, reboot the host, and close the ticket.

How the SOC Analyst Agent cuts investigation time from four hours to fourteen minutes

MFA fatigue campaigns work on a simple bet: eventually, someone taps “approve” just to make the notifications stop. It paid off. The attacker was in. The first move was quiet — deactivate SMS authentication, a small settings change easy to miss on a busy queue, and exactly the kind of thing that buys room to work without tripping an alarm. Then came the real work: AWS credentials pulled from one system, SSH keys from another, and a slow and methodical pull of internal source code.

Defending against AI-fueled social engineering

Social engineering has always been the softest edge of enterprise defense, and AI is sharpening adversaries’ attacks. Phishing, business email compromise, and impersonation still dominate the initial-access playbook, but AI has stripped out the cost, time, and skill barriers that once forced attackers to choose between reach and precision.

Security Event Management: A Practical Guide for Modern SOCs

A SOC can have broad telemetry, a modern SIEM, and a queue that still feels impossible to control. Analysts move between identity, endpoint, cloud, and network dashboards while low-confidence alerts accumulate. The problem usually isn't a lack of data. It's the missing operational layer that turns scattered events into decisions, investigations, and repeatable response. Security event management provides that layer.

Vulnerability Scanning Best Practices for 2026

Periodic vulnerability scans are no longer a reliable security program for hybrid environments. NIST's guidance treats scanning as a recurring, risk-based control that should account for changing vulnerabilities, historical results, authenticated coverage, and correlations between findings over time (NIST vulnerability-scanning guidance). Industry practice is moving in the same direction.

The New CISO Ep. 150 - Sherri Douville | Engineering Trust in AI Agents with Open-Source Tools

In this episode of The New CISO, host Steve Moore welcomes Sherri Douville for a conversation that sits outside the show's usual lane — less war story, more blueprint. Sherri works alongside CISOs rather than inside the role, and arrives with a pointed argument about what the job is becoming.

Machine vs. machine: The new reality of cybersecurity in ANZ

Frontier AI has handed attackers something they have never had before: the ability to move at machine speed. Attacks that once took days to craft now take minutes. Threats have not just evolved to be automated, adaptive, and operational around the clock. They have also changed category. We surveyed more than 850 IT and cybersecurity professionals across Australia and New Zealand to understand how organisations are keeping up. What the data reveals is not a capability problem. It is a pace problem.