Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Security Incident and Event Management.

AI in the SOC: Where security teams stand

With 96% of security teams now using AI, the question is no longer whether AI delivers real value to the SOC, but one of efficiency and reliability. The recent AI Adoption in the SOC report, conducted by Dimensional Research and sponsored by Elastic, surveyed more than 400 cybersecurity professionals responsible for security operations at companies with more than 500 employees.
Build an Intelligence Advantage with Falcon Next-Gen SIEM

Every organization has a different threat profile. Industry, geography, infrastructure, business operations, and the broader technology ecosystem all influence which adversaries and threats matter most. The challenge is putting threat intelligence to work at scale to identify the greatest threats to each business. The intelligence that security teams rely on is as varied as the threats they face.

Elastic AlertZero: Who controls AI agents in the SOC?

With Elastic AlertZero, security teams can configure agent autonomy, audit agent activity, and choose the AI models that fit their environments without being locked into a single model provider. Mike Nichols, GM of Security at Elastic, explains how AlertZero addresses three priorities for bringing agentic AI into security operations: transparency, control, and model flexibility.

Every AI Agent Creates Security Debt. Most Organizations Aren't Tracking It.

Technical debt accumulates when organizations prioritize immediate speed and defer the architectural work that keeps systems dependable. Most engineering leaders know how that story ends. The shortcuts that made the first release possible eventually slow down every release after it. The agentic enterprise is creating a security equivalent.

Is "SIEM-less" really what it sounds like?

SIEM-less security may sound like an escape from traditional SIEM complexity and costs, but the underlying capabilities still have to exist somewhere. A SIEM is a multipurpose tool. It brings together cyber and physical security use cases; drives threat detection, investigation, and response (TDIR); serves as a system of record for governance, regulatory, and compliance needs; and supports observability use cases tied to resilience and service degradation. The list goes on.

How to investigate PHP2Shell-related activity with Sumo Logic

PHP2Shell is a pair of critical flaws in the PHP interpreter itself, each with a CVSS v4.0 score of 9.2. Both let an unauthenticated attacker run code on a web server with a single crafted web request, or a pair of them, before any application code runs. Because the bug lives in PHP, not in WordPress, Drupal or Magento, every reachable PHP endpoint on an affected server is exposed, including login pages, static forms, and health checks. Every PHP release from the last decade is affected (back to 5.4).

Make Your SIEM Smarter with Cato

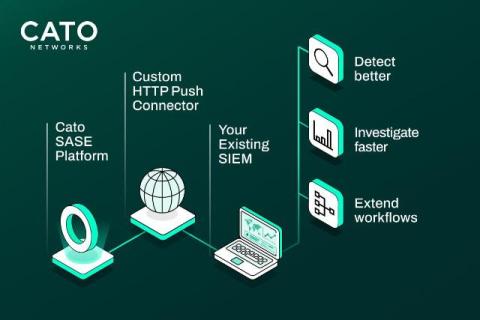
Effective security operations require more than isolated alerts. Analysts need context from across the environment to understand what happened, assess its significance, and decide what to do next. That is why accessing insights and telemetry from across your networking and security stack is critical to teams using a SIEM tool.

Security Was Built for Humans. The Enterprise No Longer Runs on Humans Alone.

Cybersecurity has spent decades learning how to distinguish trusted users from attackers. The agentic enterprise complicates that model. An AI agent can be trusted, authenticated, authorized, and functioning as designed, yet still produce an unintended or risky outcome through a sequence of otherwise legitimate actions. That scenario does not require a malicious agent.

Access Isn't Trust: A Behavioral Risk Framework for People, Service Accounts, and AI Agents

Risk in the agentic enterprise spans people, service accounts, and AI agents. All three act with legitimate credentials, so access controls alone can’t show whether their activity is safe. A behavioral risk framework applies one model to every actor: Verify expected behavior before access goes live, observe activity once it does, analyze behavior for risk and drift, and improve detection coverage over time.