Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

New 1Password SIEM integrations with Rapid7, Blumira, and Stellar Cyber

Spend less time collating security reports and investigating security issues by creating integrated, customizable dashboards with data from 1Password. The new Rapid7, Blumira, and Stellar Cyber integrations for 1Password allow you to monitor potential risks around company data or credentials stored within 1Password.
Dynamic Application Security Testing (DAST): An Overview

Dynamic Application Security Testing (DAST) is an advanced testing method that tests the production environment and analyzes application security at runtime. This type of black box testing identifies real-world vulnerabilities externally without much need for insights into the product provenance of any single component. By simulating real-world attacks in your system, DAST identifies critical security gaps that other vulnerability assessments and static methods might miss.

Cryptominers in the Cloud

Over the past decade, Bitcoin’s value has increased more than 200-fold. Similarly, other cryptocurrencies have also seen significant growth, prompting many individuals to engage in mining for profit. This rise in cryptocurrency mining has led to a substantial increase in the use of cryptominers. As organizations increasingly migrate their computing workloads to the cloud for various benefits, attackers have shifted their focus to these cloud resources for cryptocurrency mining.

Powering the future of GRC: New capabilities bring continuous visibility and automation to GRC teams

Security is a top buying requirement for businesses today. In fact, two-thirds of respondents to our State of Trust survey say that customers, investors, and suppliers are increasingly looking for proof of security and compliance. As concerns around in-house security practices, third-party tools, and access to customer data grow, customer expectations for trust continue to rise. ‍

ServiceNow Vulnerabilities: CVE-2024-4789 and CVE-2024-5217

In late July 2024, the US Cybersecurity and Infrastructure Security Agency (CISA) added two critical vulnerabilities (CVE-2024-4789 and CVE-2024-5217) affecting ServiceNow to its list of known exploited vulnerabilities. These vulnerabilities can allow unauthenticated users to execute code remotely, posing severe risks to organizations that use the platform. The potential for unauthorized access and severe data breaches makes addressing these vulnerabilities crucial.

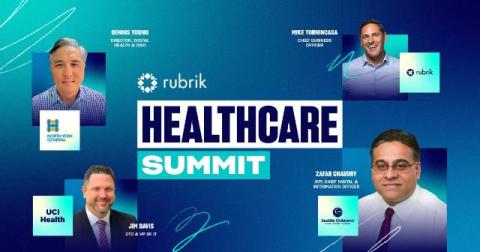
Achieving Complete Cyber Resilience in Healthcare

Ahead of Rubrik’s inaugural Healthcare Summit on September 12th, I thought it was appropriate to set the stage for what’s coming. Threat actors aren’t going to wait for you to get ready before they launch their attack. They’re banking on you not being able to recover your data—or not being able to recover fast enough—to maximize the damage they leave in their wake.

Cybercriminals Caught in the Trap: Infostealers Weaponized Against Hackers

In an ironic twist of fate, cybercriminals seeking to exploit stolen credentials have found themselves the targets of a new scheme. Security researchers recently uncovered a malicious campaign in which hackers were lured into downloading infostealer malware through a seemingly legitimate tool for checking compromised OnlyFans accounts. This development serves as a reminder that even those lurking on the dark web are not immune to digital risks.

Revival Hijack: How Abandoned PyPI Package Names Are Being Exploited to Deliver Malware

Security researchers have uncovered a novel and concerning method for cybercriminals to distribute malware using public code repositories. Known as "Revival Hijack," this technique involves the re-registration of previously abandoned package names on the PyPI repository. By taking advantage of the fact that PyPI allows the reuse of names from removed packages, attackers are able to slip malicious code into unsuspecting organizations.