Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Record of Processing Activities (RoPA): How to build and maintain it

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Browser opt-out signals arrive at scale on January 1, 2027. Here is how to know your site honors them.

If the CCPA covers your business, you must treat an opt-out preference signal as a valid request to opt out of the sale or sharing of personal information. "Sharing" includes disclosures for cross-context behavioral advertising, which is what most advertising pixels do.

CIPA for websites in 2027: what the law still covers, and how to show what your site does

If people in California use your website or app, assume CIPA applies. CIPA was written for telephone wiretapping, and courts have applied its "technology-neutral" terms to online communications for years. The business's location does not matter; the visitor's does.

Access Certification For Compliance: What IT Teams Need To Know

An access review can look complete on paper. The campaign closed, reviewers made their decisions, and the records were saved. Then an auditor asks: Who reviewed this access, what did they decide, and what happened afterward? That question can reveal problems that a completed review does not show. A rejected permission may still be active. An exception may have no clear reason. The team may also struggle to show when the review happened.

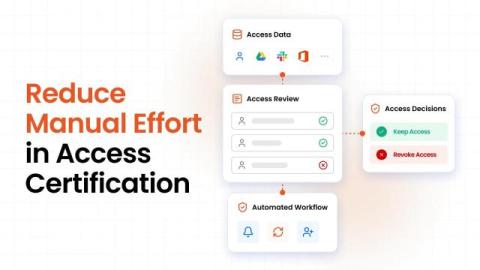
How to Reduce Manual Effort in Access Certification

Access certification can take more time than the actual review. A manager may need to review access for 50 employees. Before that happens, someone has to gather the access data, identify the right reviewer, send the requests, and track the responses. If the reviewer revokes access, someone may also need to remove it from the application. Now repeat that across hundreds of users and several applications. The workload adds up quickly.

Under CPS 234, Your APIs Are Information Assets. Can You Prove You're Protecting Them?

APRA's information security standard already covers the APIs your agents run on. Most institutions cannot yet evidence it. All APRA-regulated institutions in Australia are bound to meet CPS 234. This is the Prudential Standard for Information Security. Whether that's a bank, insurance provider, or super fund, they all fall under CPS 234, as do their third-party providers. Together, these institutions hold trillions of dollars in assets.

CISO Risk Intel Brief: Record Patch Volume, Edge Zero-Days, and AI-Accelerated Supply Chain Pressure

This briefing examines material developments across the most recent seven-day period and the preceding thirty days. It is written for executive and board consumption and focuses on residual risk, control effectiveness, material exposure, and the practical implications for application security programs, software supply chain integrity, edge and identity systems, and the accelerating role of AI in both attack and defense.

Acronis expands MDR toward broader workspace protection

Cyberattacks do not respect normal business hours: They can happen at night, on weekends and during holidays. Acronis MDR by Acronis TRU gives partners 24/7/365 expert monitoring, investigation and response without having to build their own security operations center (SOC). Acronis is expanding the MDR service with capabilities that make this expertise easier to deliver and help partners address more risks. The developments build on a broader commitment to managed security.