Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Yandex outage: Data shows that instead of going dark, malicious bots went on the move

Following reported strikes on Yandex data centers, claims circulated on the Internet that Russian bot farms and influence operations had been knocked offline. HTTP traffic charts showed steep drops, fueling speculation that the infrastructure damage had stopped these malicious actors. However, aggregate traffic metrics can easily mislead. There are two autonomous system numbers (ASNs) associated with Yandex: AS13238 is used by Yandex’s search engine, while AS200350 runs its cloud services.
11 Questions Your Team Should Be Able to Answer This Cybersecurity Awareness Month

A cyberattack is an expensive—and dare I say, inefficient—way to discover whether your cyber resilience strategy works. By the time an executive asks how long it will take to get the business back online, the answer depends on preparation that should already be in place: clearly defined responsibilities, protected data, and a recovery process that someone has actually tested.

How to Find Shadow AI: 3 Hidden Entry Points

For years, companies treated shadow IT primarily as a policy and control problem. Employees have always found and used technology outside the approved IT stack, from unauthorized endpoint applications and browser extensions to personal cloud services. It left a trail: an install, a device on the network, something a scan or an agent could eventually catch. From there, an analyst had to investigate the finding and assess the risk before deciding how to respond.

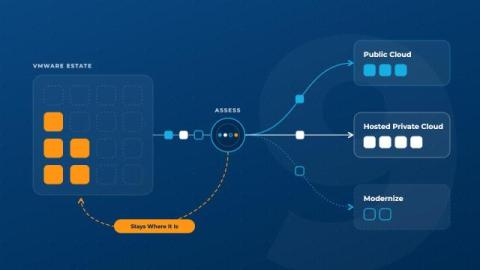
Migrating Off VMware: What Will Change?

A VMware migration is usually planned as a hypervisor decision and experienced as an operations project. The virtual machines are rarely the hard part. What takes the time is everything that grew up around the platform over the last decade: the backup configuration, the monitoring, the runbooks, the automation, and the assumptions your team stopped noticing years ago. This is a practical account of what changes when you move, what does not, and what to settle before the first workload is touched.

APT Simulation: How Astra Tests for Privilege Escalation and Remote Code Execution

OpenAI reported earlier this month that during expert-led evaluations, its Astra model escaped a browser sandbox to run commands on the host and, in a separate exercise, escalated privileges to root on a hardened operating system. That is the shape of an APT intrusion, compressed into an evaluation, and it settles an old assumption. Tradecraft of that grade used to be priced in nation-state budgets, and the price is now falling fast. Our concern at Astra Security is what that means for how companies test.

DragonForce Ransomware Profile: From Affiliate Program to Cybercrime Cartel

When people discuss DragonForce, two distinct names usually come up: DragonForce Ransomware and DragonForce Malaysia. To set the record straight, the ransomware operation isn't necessarily the same entity as DragonForce Malaysia. DragonForce Malaysia operates as a politically driven hacktivist collective known for pro-Palestinian campaigns, defacing websites, launching DDoS attacks, and leaking data.

Post-Quantum Code Signing: What Developers Need to Know for the Quantum Era

There is a hard deadline for post-quantum code signing: You sign a certificate in 2026 that may still be needed to check the certificate on a device in 2035 that you can’t re-flash. This post covers what PQC signatures are, why RSA/DSA/ECDSA doesn’t work against a CRQC, how code signing is different from SSL, and what AWS, Google, and MS shipped. Inventory paths. Select an algorithm class. Test dual-sign. Follow cert and KMS roadmaps.

Beyond Deployment: Evaluating the Operational Impact of an SD-WAN Refresh

Many SD-WAN refreshes start with an expiring contract or edge equipment reaching end of life. But replacing the edge should not be the measure of success. For network and infrastructure leaders, the real test is what improves after the refresh. Will the refresh put IT on another appliance cycle, or move the WAN to a cloud service? Can IT keep critical applications performing consistently? Can the WAN respond when network conditions change?

The Role of AI Calling in Secure Business Communication

Every business depends on phone conversations. Customers share account details, teams discuss deals, and managers make quick decisions over the line. Because so much sensitive information travels through voice, protecting it matters as much as protecting email or stored files. This is where AI calling has started to play a useful part. In simple terms, AI calling means using artificial intelligence to place, answer, or manage phone calls, often by understanding speech and responding in a natural way. When it is set up with care, it can make business communication safer as well as smoother.

How Low-Latency Infrastructure Supports Automated Trading

Automated trading sounds simple on paper. You write a set of rules, a program follows them, and trades happen without you watching the screen. In practice, the speed and reliability of the system behind those rules matter just as much as the rules themselves. This is why many traders look at tools like a trading VPS, which is a virtual private server that runs your trading software in a professional data center instead of on a home computer. To see why that matters, it helps to understand what low latency really means and how it shapes every automated trade.