Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

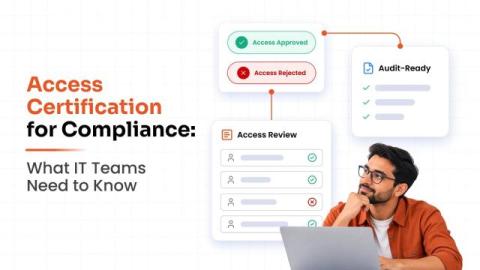
Access Certification For Compliance: What IT Teams Need To Know

An access review can look complete on paper. The campaign closed, reviewers made their decisions, and the records were saved. Then an auditor asks: Who reviewed this access, what did they decide, and what happened afterward? That question can reveal problems that a completed review does not show. A rejected permission may still be active. An exception may have no clear reason. The team may also struggle to show when the review happened.
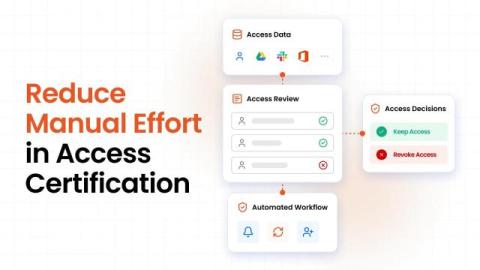
How to Reduce Manual Effort in Access Certification

Access certification can take more time than the actual review. A manager may need to review access for 50 employees. Before that happens, someone has to gather the access data, identify the right reviewer, send the requests, and track the responses. If the reviewer revokes access, someone may also need to remove it from the application. Now repeat that across hundreds of users and several applications. The workload adds up quickly.

Under CPS 234, Your APIs Are Information Assets. Can You Prove You're Protecting Them?

APRA's information security standard already covers the APIs your agents run on. Most institutions cannot yet evidence it. All APRA-regulated institutions in Australia are bound to meet CPS 234. This is the Prudential Standard for Information Security. Whether that's a bank, insurance provider, or super fund, they all fall under CPS 234, as do their third-party providers. Together, these institutions hold trillions of dollars in assets.

CISO Risk Intel Brief: Record Patch Volume, Edge Zero-Days, and AI-Accelerated Supply Chain Pressure

This briefing examines material developments across the most recent seven-day period and the preceding thirty days. It is written for executive and board consumption and focuses on residual risk, control effectiveness, material exposure, and the practical implications for application security programs, software supply chain integrity, edge and identity systems, and the accelerating role of AI in both attack and defense.

Why Choose Exabeam Over QRadar and Cortex XSIAM for SIEM?

Exabeam delivers stronger detection, faster investigations, and more flexible deployment than IBM QRadar and Cortex XSIAM. It combines user and entity behavior analytics (UEBA), Agent Behavior Analytics (ABA), and agentic AI through Exabeam Nova AI to reduce alert noise and automate workflows. With cloud-native capabilities in New-Scale Fusion, Exabeam gives security teams a modern approach to SIEM and security operations.

Why CISOs Need an Agentic SOC Strategy

CISOs need an agentic SOC strategy because traditional staffing models can’t scale to match machine-speed threats, a global talent shortage, and rising alert volume. An agentic SOC pairs AI agents that collect evidence and investigate at machine speed with analysts who provide judgment, context, and accountability. Exabeam combines Agent Behavior Analytics (ABA), Exabeam Nova AI, and automated investigation to expand coverage and speed response without adding headcount.

How Aurora Adaptive Threat Protection Spots Attacker Intent Early

Imagine this: There’s an active attack but no alert. Nothing looks wrong. Every login is valid. Every tool is trusted. Every command is one your team has run before. This invisible attack chain is how many attackers work today, and they can take control of a domain in minutes and encrypt an environment while evading traditional detections. It’s what happens between the login and the ransom note that’s the modern cyber battlefield.

How the Aurora Superintelligence Platform and Aurora Agentic SOC Help You Understand and Secure AI

AI now plays a central role in defending organizations from the modern threat landscape. It triages alerts, investigates security events, and recommends what to do next. AI is critical to defending at machine speed, but security leaders can’t see how it is making decisions on their behalf. This visibility challenge creates multiple downstream problems for security leaders that need to justify AI decisions that they can’t fully explain to their board, regulatory bodies, and insurance partners.

VMware Distributed Switch Configuration: A Complete Guide

A virtual switch is the software equivalent of a physical network switch, connecting the virtual network adapters of virtual machines (VMs) to a network at Layer 2 of the Open Systems Interconnection (OSI) model. VMware provides vSwitches across its virtualization platforms, but how you manage them depends on the type you choose. A standard vSwitch has to be set up by hand on every ESXi host.