Cybersecurity liability insurance has progressed dramatically since the first bona fide policies emerged in the late 1990s. Some of the greatest changes that have occurred in recent years include insurance companies no longer insuring against state-sponsored attacks or ransomware events. The insurers do not want to become part of a cyber-war.
There’s nothing that makes you feel older than realizing how much of your life you have dedicated to a single topic. At what point do you consider yourself an expert? After more than 17 years in vulnerability management, I’m starting to come around to the idea that I might be an expert in the field. Although, the main reason I feel that way is because, at this point, I’ve seen pretty much everything.
In a chilling reminder of the relentless threat posed by hackers and cybercriminals, not even the aviation industry is safe from their clutches. Recent reports have shed light on a grave security breach, as unauthorized individuals gained access to vital pilot credentials within two prominent American aviation companies. The far-reaching impact of this breach serves as a stark warning to businesses across all domains: no data is safe from the clutches of malicious actors.
Truebot infects networks throughout the US and Canada, Charming Kitten targets new operating systems, and SmugX targets European government entities.
Business Email Compromise (BEC) is a targeted cyberattack in which a cybercriminal poses as a trusted figure, such as the CEO of a company, and sends out an email to specific individuals requesting sensitive information or money. BEC attacks involve research and preparation in order for the cybercriminal to develop a convincing impersonation. Continue reading to learn more about business email compromise and what organizations should do to prevent this type of attack.
Implementing an AWS multi-account strategy is a popular approach that helps organizations to manage their cloud resources efficiently. In my previous post, I discussed our reasons for implementing an AWS multi-account strategy, our journey, and some of the benefits we gained as an organization. However, implementing this strategy can come with its fair share of challenges.
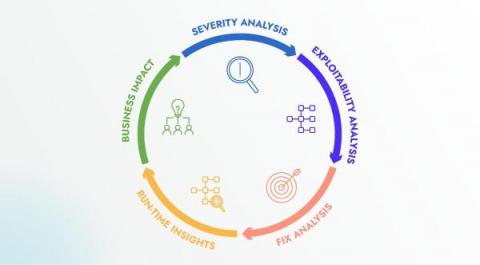
Relying solely on the Common Vulnerability Scoring System (CVSS) is insufficient when it comes to effective vulnerability management. While the CVSS score provides a quantitative measure of a vulnerability’s severity, it fails to capture the contextual nuances that can significantly impact the actual risk to an organization. In this article, we will discuss how best to choose a vulnerability management solution.
ARx is a healthcare provider based in Kansas. The company specializes in drug delivery systems and works with many different healthcare facilities. During regular work, the company handles patient information and is in charge of healthcare details as well as personal information. According to ARx, it was hacked in 2022, and nearly 40,000 people could be exposed because of the attack.
With more than 2.5 million cybersecurity positions unfilled globally, the cybersecurity field is facing a severe shortage of talent, with an increasing demand for skilled professionals to combat the ever-evolving threats in the digital landscape.