Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

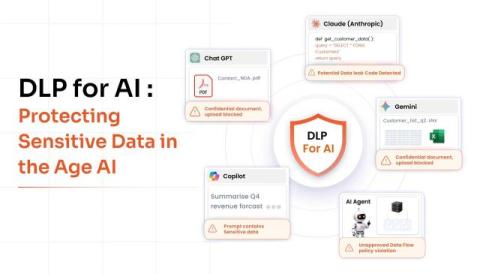
DLP for AI: Protecting Sensitive Data in the Age of AI

Employees paste code into ChatGPT. They drop customer lists into Gemini for a quick summary. They upload a contract to an AI note-taker before a meeting starts. None of it feels risky in the moment. But all of it can walk sensitive data straight out of your organization. AI DLP exists to close that gap.
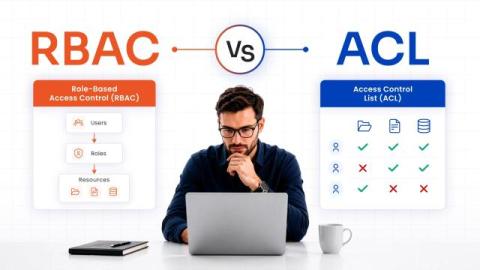
RBAC vs. ACL: Understanding the Differences in Access Control

Every employee, contractor, application, and device in your environment needs the right level of access, but deciding how that access is managed is where many organizations struggle. Grant too many permissions, and you increase security risks. Make access too restrictive, and productivity suffers. Understanding the differences between RBAC and ACL is essential for designing a secure, scalable, and compliant access strategy.

Erasing Security Debt with an App Risk Remediation Platform

A risk remediation platform is the operational infrastructure that transforms security debt from an unmanaged backlog into a structured, measurable program. With 82% of organizations now carrying security debt and the average fix half-life sitting at 243 days, the gap between vulnerability discovery and resolution is where breaches happen.

Top 5 Custom Software Development Companies in the UK; Reviewed and Ranked

Picking the right custom software development partner plays a noticeable role in whether a digital transformation project delivers long-term business value or is just an expensive setback. The best consultancies combine technical expertise with strategic thinking, helping companies modernise legacy systems, streamline operations, and build scalable applications that support future growth. But, picking the best custom software development company often feels overwhelming.

8 Modern Consumer Habits That Include Tools Like Subdelete

Recurring payments have become part of everyday spending. Streaming services, cloud storage, fitness memberships, delivery plans, and work apps may renew on different dates. Each payment can seem small on its own. Together, they can take a noticeable part of a monthly budget. Subdelete prepares and sends a formal cancellation notice and provides a delivery record. It fits into a larger process that begins with finding unused services and ends with checking that billing has stopped..

Why Continuous Security Validation Matters for Enterprise Protection

Enterprise protection can appear sound during audits, yet routine change can weaken safeguards between those checkpoints. A cloud setting shifts, a user role expands, or a device enters service without full review. Each event can alter exposure in ways teams do not see right away. Continuous security validation matters because it checks present conditions, rather than past assumptions. That ongoing proof helps organizations identify weak coverage early and reduce avoidable operational harm.

8 Fleet Cybersecurity Metrics Worth Tracking

Running a modern fleet involves far more technology than it did a decade ago. Vehicles now connect with GPS devices, mobile apps, cloud platforms, maintenance software, and outside service providers. Those tools make routine work easier, but every connection also creates another place where credentials, equipment, or sensitive information could be exposed.

Why Every Company Should Consider Random Drug Testing

Maintaining a secure office space requires proactive steps from modern business leadership. Many corporate owners overlook the daily workplace hazards that unaddressed substance issues can easily create on the job site. Lack of awareness can lead to severe operational setbacks for the entire company. Implementing smart safety measures protects your valued workforce and your bottom line. Random screenings offer an unbiased path toward a cleaner, more focused work environment for everyone. Taking action now positions your enterprise for long-term operational success.

Quantum Security Threats to Encryption Systems: Why RSA and ECC Are No Longer Enough

For nearly fifty years, RSA and ECC have quietly protected your bank logins, medical records, and government secrets. That trust is now expiring. In May 2025, a researcher at Google Quantum AI showed that a 2048-bit RSA key could be cracked by a machine with fewer than a million noisy qubits, roughly twenty times less hardware than the same scientist estimated back in 2019. Problems that once kept attackers out for billions of years are sliding toward solvable in days. Worse, sensitive data is already being stolen and stockpiled for a future decryption payday.

7 AI Governance Tools for Shadow AI Detection

AI adoption has accelerated faster than most organizations’ ability to manage it. Security and compliance teams are now responsible for overseeing machine learning models, large language models (LLMs), agentic AI systems, and shadow AI — often with frameworks and processes that weren’t built for any of it. The gap between deploying AI and governing it responsibly is where risk lives. AI governance tools exist to close that gap.