Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

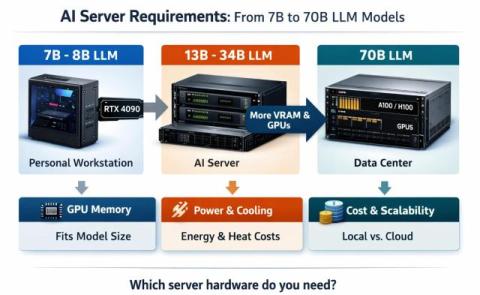
What Server Do You Need to Run an AI Language Model?

Running your own AI model sounds exciting, but one question appears almost immediately: what kind of server do you actually need? A small language model can run on a personal workstation, while a large 70B parameter model may require enterprise-grade GPUs and expensive infrastructure. Choosing the wrong hardware can lead to wasted money, unnecessary complexity, or disappointing performance.

Top IT Outsourcing Companies in the USA

Finding an IT outsourcing vendor takes an afternoon, but choosing the right one takes longer. The US market is crowded with companies that offer custom software development, dedicated teams, and endtoend delivery. Many look interchangeable. But in practice, the differences are significant: a vendor strong in healthcare SaaS may have little experience with enterprise legacy systems, and a team built for startup MVPs may struggle as scope, integrations, and compliance demands grow.

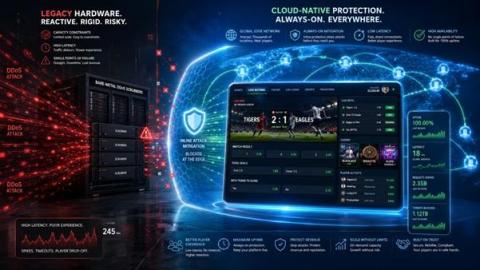
Why iGaming operators choose Cloudflare Enterprise over bare-metal DDoS scrubbers

A slot machine that stalls for three seconds during a jackpot spin loses more than a session. It loses a customer - often for good. That's the brutal math behind DDoS defense in online gambling, where uptime isn't a metric, it's the product. And increasingly, operators are betting on cloud-native protection over the racks of scrubbing hardware that used to define this space.

Building Secure Server Rooms: Why Physical Infrastructure Matters as Much as Cybersecurity

What do most IT managers worry about? Ransomware attacks, zero-day exploits, phishing scams. What don't they talk about? Shelves creaking under a rackload of servers, UPS batteries left on the floor out of sight until they're needed. Yet such oversights are just as dangerous as cyberattacks, and easier to solve. While cybersecurity takes all the glory, the physical infrastructure of your server room is often as crucial for its protection and operation.

Exploring the Advancement of Wireless Mouse Technology

In today's digital era, efficient computer interaction has become an essential part of daily life. Among the devices that support this seamless experience, the wireless mouse stands out as a significant innovation. By removing the limitations of traditional cables, it provides users with greater flexibility, improved mobility, and a more organised workspace.

LimeRat Malware: Delivery Techniques and Organizational Impact

Lime RAT stands out as an openly available and meticulously documented malware suite built on the.NET framework, boasting a multitude of capabilities that can be highly destructive when wielded proficiently. Its capacity to pilfer a wide array of valuable data, employ encryption for ransom purposes, or transform the targeted host into a basic-capability bot, combined with an easy-to-use control panel interface, positions it as a preferred choice for less experienced operators.

Emerging Threat: (CVE-2026-56291) Balbooa Forms Remote Code Execution via Unauthenticated File Upload

CVE-2026-56291 is an unauthenticated arbitrary file upload vulnerability in Balbooa Forms, a commercial drag-and-drop form builder for Joomla installed as the com_baforms component. The flaw is classified as CWE-434, unrestricted upload of a file with a dangerous type. The vulnerability carries a CVSS v3.1 base score of 9.8 (Critical). It has also been assigned a CVSS v4.0 base score of 10.0 (Critical), with an exploitation maturity of “attacked.”

NIS2 compliance for health care MSPs: what you need to know and do

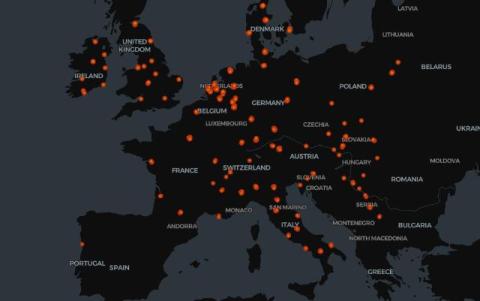
Twenty of 27 EU member states had transposed the NIS2 Directive into national law by January 2026 (Wavestone, NIS2 transposition status, 2026). The remaining seven are under formal infringement proceedings from the European Commission. If you run an MSP serving health care clients in the European Union, NIS2 compliance is no longer a regulatory horizon problem. It is the operating environment.