Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Rise of Rogue AI Agents. What Recent Incidents Tell Us About the Modern World of AI

AI! It's in everything, everywhere, all at once! It’s reading emails, summarising meetings, drafting documents, and writing code, and it’s no longer just giving us answers. We now also have agents that act on their own, access other systems, and make decisions with little to no human oversight.
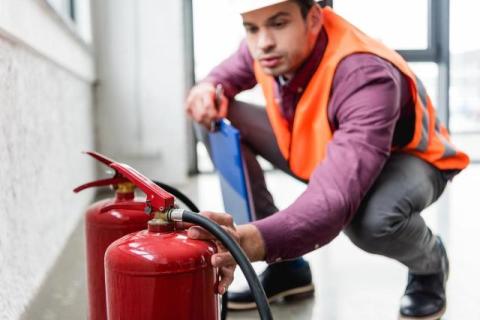
5 Reasons a Security Guard Cannot Legally Replace a Fire Watch Guard

With a malfunction in a fire alarm system, the main fire line breaks, or life safety control panels become non-functional due to maintenance work, there will be a requirement for compliance immediately. In order to save time and money, facility directors usually rely on the security guards who perform their duties in the building to "watch out for any fires.".

How Do Insurance Companies Decide What Vehicle Repairs They'll Cover After an Accident?

After a crash, most people assume the insurance company will cover the damage, and that'll be the end of it. That assumption runs into reality fast. Insurance companies don't just write a check for whatever the shop quotes - they follow a defined process built around policy terms, liability findings, and vehicle valuation methods that can cut your settlement well below what you actually need. Understanding how that process works puts you in a far stronger position, whether you're filing a claim through your own insurer or pursuing the at-fault driver's policy.

What is Compliance Monitoring? Challenges, Solutions, Tools

As data privacy frameworks expand and operational risks evolve, security leaders and compliance officers face an ongoing challenge: Maintaining total visibility across employee activity, sensitive data, and internal controls without slowing down business operations. Compliance monitoring bridges the gap between policy and practice, giving organizations the proactive foresight needed to detect risks before they trigger costly violations.

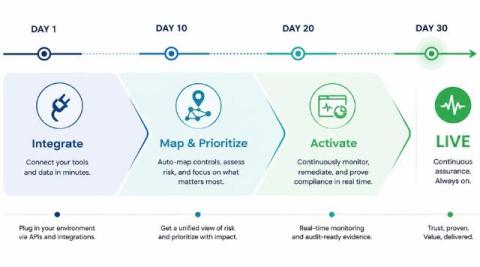
How to implement continuous control monitoring in 30 days

Continuous control monitoring may sound like a program you have to rebuild your whole GRC function to reach. It isn’t. It’s a phased build that integrates with the systems you already run, and a focused team can have continuous monitoring live across its priority controls in about a month.

How AI Governance Reduces Security Risks

AI governance reduces security risk by enforcing least-privilege access, protecting the data and credentials AI systems handle and making every AI action auditable. This matters because most organizations deploy AI faster than they can govern it. Employees adopt unsanctioned tools, and autonomous AI agents are created under existing user identities. Each one adds unmonitored machine identities that expand your attack surface – the exact gap that governance closes.

The Blind Spot: How "Bulletproof" Phishing Redirectors Slip Past SEGs

By Shikhar Dalela and Jeewan Singh Jalal The operators named the kit themselves. Buried inside compromised legitimate websites, the hidden staging directory is sometimes literally called “/.bulletproof”, and the PHP session cookie the kit sets on every visitor is named “bp_redir_sess.” The “bp” stands for bulletproof, which is an unusual degree of candor from a threat actor whose entire design philosophy is concealment.

Introducing Real-Time Coaching in KnowBe4's AI-Native Security Awareness Training

Attackers are getting smarter. AI is making social engineering more convincing, more personalized, and harder to spot than ever before. Training the digital workforce, employees and agents, to recognize threats is necessary, but even the most security-conscious users can still make a mistake at the moment of risk. Workforce risk is a behavior change problem, and effective behavior change requires knowledge, pressure-tested application and real-time reinforcement all working together.

Episode II: Attack of The Claudes

Two weeks after Hugging Face disclosed an AI-driven intrusion into part of its production infrastructure, Anthropic said it had found three incidents from its own cyber evaluations. Hugging Face traced its compromise through a data-processing pipeline, where a malicious dataset abused a remote-code dataset loader and a template-injection issue in a dataset configuration.