Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The AI notetaker you can't see in the participant list

For about three years, the governance question around AI meeting assistants had a convenient property: you could see them. The tool joined the call as a named participant. It appeared in the attendee list. Everyone in the meeting had at least the theoretical opportunity to object, and a security team reviewing an incident could reconstruct which meetings had been recorded by looking at who else was in them.
Many New Technologies, Products, and Tools for Modern Protection Programs in New York, New Jersey, and Florida

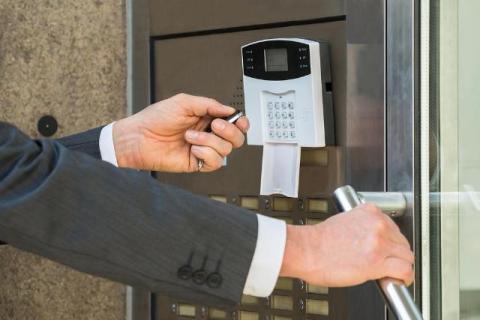
A lot of buyers still start with the most visible layer of protection: cameras, guards, or a front desk presence. The real gap usually sits behind that first impression. If doors, credentials, visitor flow, and response routines are loose, the rest of the program ends up documenting problems instead of preventing them.

Why Modern Email Security Requires More Than Sender Reputation

For years, email filtering worked from a stable premise: malicious messages would expose themselves through something observable. A suspicious domain, a spoofed sender, a known-bad attachment or a URL with poor reputation gave defenders a concrete signal to block. Those controls still stop commodity phishing. What has changed is that many convincing attacks now inherit trust rather than imitate it.

What Is PCI DSS Compliance? the Essential Guide

You're reviewing payment flows, the bank has asked for proof, and the audit deadline suddenly feels real. The problem isn't usually that the team has done nothing, it's that nobody has turned day-to-day security work into evidence a card brand, acquirer, or assessor can use. PCI DSS compliance is where that gap gets exposed, and it's why security teams that already run SIEM, XDR, or EDR still get pulled into a separate compliance scramble.

How Regulated Data Leaks Through AI, One Paste at a Time

A support coordinator has a difficult letter to write. The customer record is open in one tab, a consumer AI assistant in another, and the deadline is this afternoon. She selects the record, copies it, pastes it into the prompt box, and asks for a polite draft. Thirty seconds later she has a good letter and a regulatory problem, and nobody in the organization knows about either. ‍ The sequence below traces that single action through to its consequences.

Cyber Risk Appetite Statements That Can Be Breached

Most cyber risk appetite statements cannot be breached. A board approves language about maintaining a low tolerance for disruption, the statement enters the policy library, and no observable event in the following three years violates it. A statement no event can cross is a value rather than a control. ‍ Making one testable requires four terms that get used interchangeably and mean different things, thresholds expressed in units something can exceed, and a defined response for when it does.

What is Endpoint Monitoring? Tools, Processes, Challenges

The traditional network perimeter is dead. In an era of hybrid work, cloud proliferation, and sophisticated insider threats, every laptop, server, and remote device connected to your system represents a potential attack vector. Endpoint monitoring has become an indispensable baseline for enterprise security, providing security leaders with continuous visibility into employee and device activity.

CVE-2026-58048: cPanel & WHM Database Privilege Escalation Vulnerability

Hosting environments run on a basic assumption: an account with limited permissions should stay limited. CVE-2026-58048 breaks that assumption inside cPanel & WHM. Any authenticated account with MySQL or MariaDB feature access, including a standard low-privilege hosting account, can now escalate to root-level database privileges through a database rename operation. A public proof-of-concept already exists, which means the barrier to exploitation is low and the window to act is short.

Windows Event Log Analysis: A Practical Guide

If you're staring at a flood of Windows telemetry at 2 AM, the problem usually isn't that the logs are useless. The problem is that nobody turned them into a workflow. Raw Security, System, PowerShell, and Defender events can tell you exactly what happened, but only if collection, parsing, triage, and reporting are handled like part of the same control, not four separate chores.

Best AI Governance Platforms and Software (2026 Comparison)

You approve five AI tools; your employees use 20. According to UpGuard's State of Shadow AI report, 81% of the workforce is already bringing unmonitored AI tools to work, and legacy security tools are leaving massive gaps in workforce Shadow AI and regulatory compliance. Modern AI governance platforms give you real-time visibility and runtime guardrails to close that gap. They back it up with automated auditing, so you have evidence when someone asks for it.