Mailchimp
Not subscribed to OpsMatters Newsletter


The world of cybersecurity has been constantly challenged since the pandemic started. With the dust still settling, a new concern has taken the entire cyber landscape by storm. A flaw in Log4j, a widely used Java-based logging library, allows hackers unbridled access to computer systems. The vulnerability (CVE-2021-44228) affects everything from the cloud to security devices. Attackers have come up with worms that can spread independently from one vulnerable system to another.
Fairwinds Insights is Kubernetes governance and security software that enables DevOps teams to monitor and prevent configuration problems in their infrastructure and applications. Not only does Fairwinds simplify Kubernetes complexity, but it also reduces risk by surfacing security and reliability issues in your Kubernetes clusters.
The situation involving the log4j ( log4shell ) vulnerability has been rapidly evolving since its release a little over a week ago. A new exploit, CVE-2021-45046, was found which was not covered by the initial 2.15.0 patch. Not long after the 2.16.0 patch was released, another issue was found, CVE-2021-45105, which resulted in the release of 2.17.0. There is clearly a lot going on in the log4j library.
Humio is a CrowdStrike Company. Data logging is the process of capturing, storing and displaying one or more datasets to analyze activity, identify trends and help predict future events. Data logging can be completed manually, though most processes are automated through intelligent applications like artificial intelligence (AI), machine learning (ML) or robotic process automation (RPA).
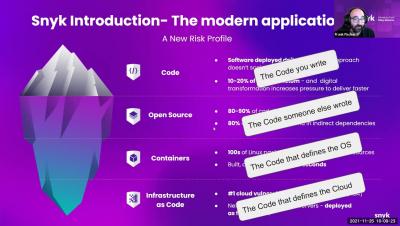
More than 90% of organizations rely on open source software, a reliance that introduces a significant amount of security and legal risk via either direct or transitive open source dependencies. To overcome this challenge, Software Composition Analysis (SCA) solutions are playing an increasingly important role in helping organizations successfully identify and mitigate potential security issues.
Starting in early 2021, Snyk Code and became available as a freemium offering for Snyk users. Snyk Code helps developers quickly and accurately find, prioritize, and fix security flaws in proprietary code. With detailed remediation guidance at every stage of the software development lifecycle (SDLC), from the developer’s environment (IDE) to continuous integration and development (CI/CD) pipelines, Snyk Code revolutionizes static application security testing (SAST).