Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Autonomous SOC Was a Promise SOAR Never Kept

David Melamed is Head of Emerging Technologies at Torq. He joined through Torq’s acquisition of Jit, which he co-founded and has led as CTO since 2020, building agentic security on a production Context Graph. A cloud security veteran with 20+ years of experience, David previously held senior technical roles at Cisco (via the CloudLock acquisition) and MyHeritage. For all the gods and monsters in The Odyssey, the ship mostly moves for one reason: men row it.
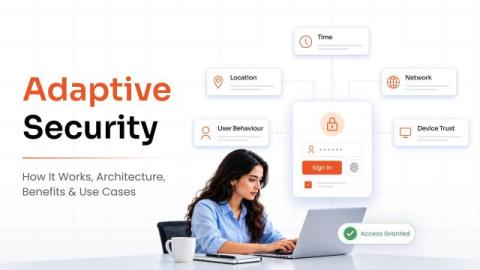
Adaptive Security: How It Works, Architecture, Benefits & Use Cases

Adaptive security is a cybersecurity approach that continuously monitors users, devices, networks, and security events to identify risks and adjust defenses in real time. Unlike static security models that rely on fixed rules and periodic updates, adaptive security responds to changes in behavior, context, and threat levels as they occur. It continuously evaluates security risks, detects unusual or suspicious activity, and adapts security controls based on the situation.

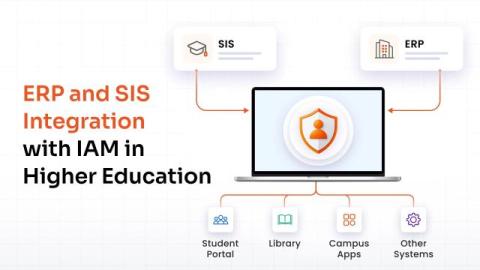
ERP and SIS Integration With IAM for Higher Educational Institutes

Higher education institutions manage identity information across systems such as Enterprise Resource Planning (ERP) platforms, Student Information Systems (SIS), and HR systems. These records determine whether someone is a student, employee, faculty member, researcher, alumnus, or another type of campus user. Integrating these systems with Identity and Access Management (IAM) lets institutions use those records to manage digital identities and access throughout the user lifecycle.

Who owns your AI agents? Probably no one

AI agents are multiplying faster than most organizations can track, let alone govern. IDC predicts there will be 1.3 billion agents by 2028. Every team that adopts one is also, often without meaning to, creating a new identity. And it’s one that can access systems, move data, and act on someone's behalf. The rush right now is to get ahead of that before it spirals, and the first step is to answer a basic question: whose job is this?

Cybersecurity Budget Planning for 2027

A budget presented as a total invites one question with two answers, approve or reduce. A budget presented as a ranked list invites a different question, which is where to draw the line, and that is a decision a board can make rather than a negotiation it can only win or lose. ‍ The ranking comes from one calculation per candidate control. Expected loss before, minus expected loss after, divided by cost. Order the list by that ratio and the budget builds itself, including the part that says stop.

Why Security Controls Need a Source of Truth | Garrett Hamilton on TAG Infosphere

Every security team has a source of truth for its assets and its identities. Very few have one for how those assets are protected. Here Garrett explains what that source of truth has to look like and why it has to be deterministic. Garrett joined Ed Amoroso of TAG Infosphere for a wider conversation on AI, security controls, and assurance. The full interview covers.

Falcon Guardian: Claude Code Hooks Demo Drill-Down

Claude Code reads your developers' files and runs commands in their shell. A Social Security number pasted into a prompt or an API key in a.env file can reach the model, and a single force push can overwrite a shared branch. This demo shows how to secure Claude Code with CrowdStrike Falcon Guardian. Claude Code Hooks run a check at set points, such as when a developer submits a prompt or before a tool runs. Falcon Guardian uses those hooks to check prompts and tool calls against a central policy, deployed through Claude Code's managed settings file so developers can't override it.

From IT Provider to Security Partner: The Evolution of MSP Cybersecurity - The 443 Podcast - Ep. 391

In this episode, WatchGuard CSO Corey Nachreiner sits down with Andrew Morgan, founder of Right of Boom, to discuss the evolving role of MSPs in cybersecurity live from Impact Partner Conference in Nashville. From common security gaps and lessons learned from real-world incidents to the impact of AI, Andrew explores what it takes for MSPs to move beyond selling security tools and become true security providers. Tune in to learn how MSPs can better protect themselves and their customers while preparing for the challenges ahead.

The Top AI Coding Agent Risks And How To Mitigate Them

AI coding agents are now writing and shipping code with far less human review. Is your security keeping up? Veracode CISO Sohail Iqbal breaks down the top security risks of AI coding agents and agentic AI, and what security teams should put in place first. If code is written at machine speed, it has to be remediated at machine speed. What you will learn: Chapters: Subscribe for more insights on Application Security, AI Coding, and DevSecOps.