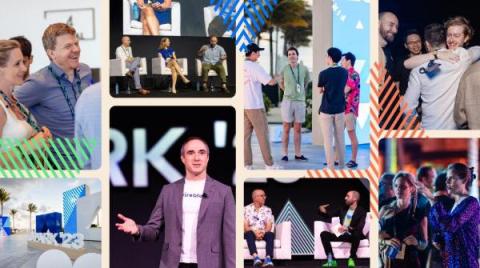
Fireblocks’ second annual user conference, SPARK ‘23, saw nearly 600 attendees representing over 300 companies in the digital asset and crypto space. Kicking off the conference was the welcome reception, which featured a spectacular drone show. The display set the tone for what SPARK is about – innovation and community. The conference empowers customers to maximize the full potential of the Fireblocks platform while forging new alliances with fellow leaders.
Microsoft implements enhanced connection and encryption and removes outdated SMB1 firewall rules to improve Windows 11 security. Microsoft’s most recent Windows 11 Insider Preview Build includes a significant change to handling firewall rules, especially the outdated SMB1 protocol. By mimicking the actions of the Windows Server “File Server” role, the new method seeks to give customers a better level of network security.
In the fast-paced environment of cloud-native apps, security and seamless connections are a priority. Many DevOps and SecOps professionals use Kubernetes native features to handle their container security, keeping a tight grip on access and secrets to improve security posture. The integration between AWS AssumeRole and JFrog Access in Amazon Elastic Kubernetes Services (EKS), enhances enterprise security by automating secrets management.
Apache has released an advisory for a critical vulnerability discovered in Struts versions 2.0.0-2.3.37(EOL), 6.0.0-6.3.0.1 and 2.0.0-2.5.32. This vulnerability is being tracked as CVE-2023-50164 with a CVSS score of 9.8 (Critical) and is reportedly being actively exploited. Impacted versions are affected by a file upload and directory traversal vulnerability that can lead to remote code execution.
Kroll forensic examiners and threat intelligence analysts identified a new phishing tactic targeting individuals using QR codes. Victims receive phishing emails impersonating Microsoft, letting them know that additional security measures are required and asking victims to scan the QR code in the body of the email or the email attachment.
One recurrent point in our first interaction with Kubernetes users is the difficulty of implementing security controls on their Kubernetes clusters where tenant or workload isolation is required during rollout or runtime. This happens due to one of the following reasons: Calico provides several features and capabilities to cover each one of the above points with Policy Recommendation, Policy Board, and Dynamic Service and Threat Graph.
Artificial Intelligence is revolutionizing everything and cybersecurity is no exception. A growing number of industry experts and professionals are beginning to reflect on the benefits and risks of this innovative technology within the cybersecurity framework. AI can be used to enhance protection for businesses against threats but, on the flip side, it can also be applied to refine cybercriminal attacks.