Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

CISO Risk Intel Brief: Material Exposures, Control Gaps, and Program Response

This executive intelligence briefing covers two distinct horizons: the past week (12–19 August 2026) and the past month (approximately 20 July–19 August 2026). It prioritizes AppSec, software supply chain, state-actor activity, cloud/IaC, identity, ransomware resilience, and regulatory developments with board-level implications. Analysis focuses on residual risk, control effectiveness, and business enablement rather than volume metrics alone.
Coding Agent Risk for CISOs: Blast Radius, Governance, and Where to Start

Claude Code, Cursor, GitHub Copilot, and Gemini CLI are running on developer machines across your enterprise right now. They're browsing the web, writing to your filesystem, committing code to your repositories, and calling external APIs under the identity of your engineers. Most security teams have no visibility into any of it. This isn't a future problem.

The New CISO Ep. 149 - Ravi Soin | Don't Be a Risk Manager. Be a Trust Architect.

Ravi Soin has clear advice for anyone starting a security career today: don't be a risk manager, be a trust architect. In this episode, Steve Moore sits down with Ravi—CIO and CISO at Smartsheet—for a builder's-eye conversation on the modern CISO role, AI as an accelerant on old sins, and why the CISO who still says “no” is already obsolete.

Operationalizing Secure by Design: a CISO's guide to closing the gap between policy and reality

We’ve been listening to dozens of CISOs. In roundtables, peer forums, customer and prospect calls, on the record, off the record, at event floors and dinners. And the same thing keeps coming up: the security program on paper and the one running in production are rarely the same. There’s a gap between security policy and reality.

CISO Risk Intel Brief: Application Risk Intelligence for Early August 2026

Senior security leadership continues to confront a dual acceleration: self-propagating software supply-chain worms that weaponize developer credentials at unprecedented velocity, and the persistent security debt introduced by AI-generated code. This briefing synthesizes material developments across the most recent seven days and the preceding thirty days, framed strictly around residual risk, control effectiveness, and business enablement.

Shadow IT in the Interconnected Web: A CISO Advisor's View

On World Wide Web Day (August 1), it’s worth celebrating what the web has made possible. It enabled remote work to function at scale, SaaS platforms to deliver capabilities in days instead of months and instantaneous collaboration through shared docs, chats, whiteboards and task tools that update in real time.

CISO Executive Briefing: Application Risk Intelligence for July 2026

This briefing synthesizes verified threat activity, vulnerability disclosures, supply-chain incidents, and regulatory signals into a board-ready assessment of residual risk and control effectiveness for the period of 29 June to 28 July 2026. The analysis prioritizes AppSec, software supply chain, identity, cloud/IaC, API/web, ransomware resilience, and AI-related exposure.

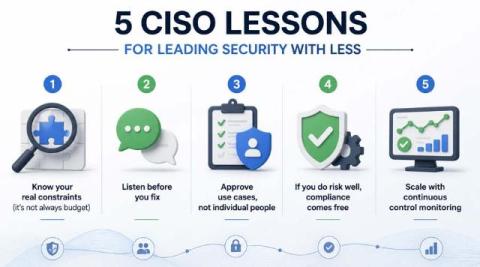
5 CISO lessons for leading security with less

Every CISO knows they need to do more with less. Fewer analysts, tighter budgets, more obligations. Matthew Martin has led security through all of it in two very different worlds: 20 years in financial services, and now in higher education at Western Carolina University. After two decades with enterprise budgets and every tool available, Matt made a deliberate choice to take on higher ed with different constraints and a decentralized structure.