Security | Threat Detection | Cyberattacks | DevSecOps | Compliance


How We Built SELinux Support for Kubernetes in Gravity 7.0
As one of the engineers on the Gravity team here at Gravitational, I was tasked with adding SELinux support to Gravity 7.0, released back in March. The result of this work is a base Kubernetes cluster policy that confines the services (both Gravity-specific and Kubernetes) and user workloads. In this post, I will explain how I built it, which issues I ran into, and some useful tips I’d like to share. Specifically, we will look at the use of attributes for the common aspects of the policy.
Network Security for D2iQ Konvoy
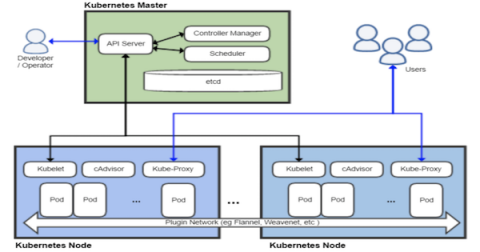
Approaching Kubernetes Security - Detecting Kubernetes Scan with Splunk
The Kubernetes framework has become the leading orchestration platform. Originally developed by Google, Kubernetes is a "platform for automating deployment, scaling, and operations of application containers across clusters of hosts" * . The kubernetes platform is used in all Cloud platform provider vendors as a tool that allows orchestration, automation and provision of applications and specific needs computing clusters and services.
How to Implement Network Policy in Google GKE to Secure Your Cluster
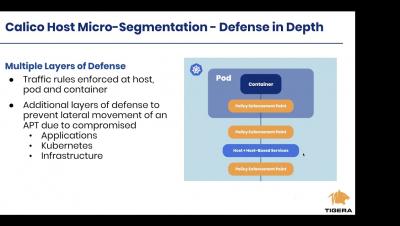
Getting up and running with Calico Host Micro segmentation Protection on AWS
Calico Enterprise 3.0 - Global Network Security Center for Kubernetes
As our enterprise customers build out large, multi-cluster Kubernetes environments, they are encountering an entirely new set of security challenges, requiring solutions that operate at scale and can be deployed both on-premises and across multiple clouds.