Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

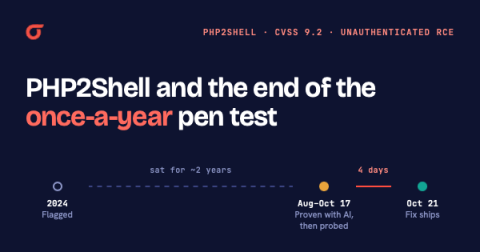
PHP2Shell and the end of the once-a-year pen test

On October 21, 2026, PHP shipped emergency fixes for two flaws that let anyone on the internet run code on a PHP web server, with no login. The weakness behind them had been flagged in 2024 and then sat, partly because nobody had proved it was exploitable. In 2026, researchers working with AI models proved it within days. Exploit attempts started before the fix shipped, and details leaked a day ahead of schedule. That sequence is the real story of PHP2Shell. The bug matters, but speed matters more.
One Password to Rule Them All

What if you only had to remember one password for the rest of your life? A password manager makes that possible. Keeper Security stores your passwords in an end-to-end encrypted vault with zero-knowledge architecture, meaning not even Keeper can see what's inside. You get strong, unique passwords for every account synced across all your devices, and peace of mind knowing your digital life is locked down.

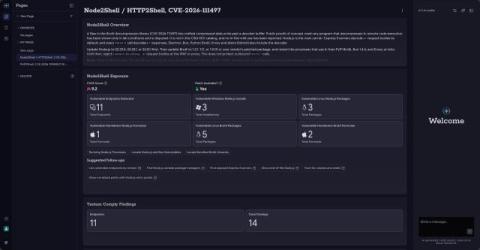
HTTP2Shell: Find and Fix Vulnerable Brotli Copies with Tanium

If you run Node.js, update to 26.12.1, 24.22.1 or 22.23.4 now. If you run Python, upgrade the Brotli package to 1.2.1 and brotlicffi to 1.2.1.0. If you run Bun, move to 1.4.4. All three carry a fix for CVE-2026-111497, an out-of-bounds write in Google's Brotli decoder that can let a remote, unauthenticated attacker crash a process, read its memory or potentially run code by sending it crafted compressed data. Google's CVE record scores it 9.2 under CVSS v4.0.

eMudhra CA Compromise: Find and Fix Your Exposure with Tanium

On October 17, 2026, a researcher reported that eight intermediate certificate authorities (CAs) run by eMudhra have private keys that anyone can calculate from the public certificates. Six of the CAs are for TLS (website) certificates and two are for code signing. Sectigo cross-signed the same eight keys, so 16 certificates are affected in total With these keys, anyone can issue a certificate for any website, or sign software, and it chains to root CAs that many systems trust.

Home Security Mistakes That Can Put Your Property at Risk

Keeping a home secure involves more than installing strong locks or purchasing a security camera. Many vulnerabilities develop through everyday habits, overlooked maintenance, and decisions made when renovating or improving a property. Even homeowners who invest in modern security technology can leave certain areas exposed without realizing it.

Top 5 Minimalist iPhone Duo Case Designs

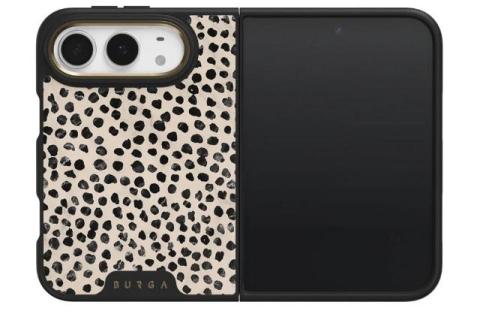
I'll admit it: the first time I saw the iPhone Duo folded shut on a desk, my thought wasn't "what case should this go in?" It was "please don't put anything loud on that." It's a tidy-looking phone. Titanium edges, two muted colors, and a hinge you barely notice once it's closed. Turns out a lot of people are in the same headspace. Fortune Business Insights puts the minimalist lifestyle products market at roughly $11.5 billion this year, and it expects that number to hit $20 billion by 2034. So, yes, owning fewer but nicer things has gone well beyond a Pinterest phase.

How Network Discovery Tools Map Every Device on a Company Network

A company network changes as staff connect laptops, printers, phones, servers, and virtual machines. Some devices remain for years; others appear briefly during projects, maintenance, or seasonal work. An incomplete inventory can leave an unmanaged endpoint exposed or slow an investigation. Network discovery gives IT teams a repeatable way to identify equipment and record details they can verify and maintain. The process starts with scans, but a useful map depends on what happens after detection.

PHP2Shell: Exposure and Response with the CrowdStrike Falcon Platform

PHP2Shell (CVE-2026-109618 and CVE-2026-109619) introduces two critical remote code execution vulnerabilities affecting PHP, making it important for security teams to identify affected systems, understand their exposure, and investigate potential exploitation.