PCI DSS, or the Payment Card Industry Data Security Standard, is the set of regulatory requirements all organizations who process card payments must adhere to. Sounds simple enough, right? But PCI compliance can pose a major challenge to organizations if they’re not equipped with the proper knowledge and tools.
The Payment Card Industry Data Security Standard (PCI DSS) program provides an information security compliance benchmark for companies that are handling, processing and storing cardholder data online. Software development and vulnerability management are covered in the PCI DSS compliance requirements as this concerns products and applications created to handle cardholder data.
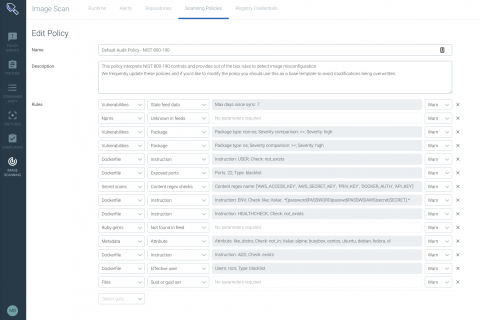
Today we are very excited to announce our latest release — Sysdig Secure 2.3! In this version of Sysdig Secure, we have invested heavily in hardening the compliance posture of Kubernetes, Docker configurations, and container images. We have released a set of features that provide compliance focused image scanning, guided remediation, compliance dashboards, and more.
Despite the fact that PCI DSS has been in effect for over a decade, and most merchants are achieving compliance, some of the world’s largest retailers have been hit by to data breaches. The sad truth is that achieving compliance doesn’t guarantee data protection, even for large organizations. For example, more than five million credit card numbers were stolen in 2018 hacks of two major retailers.
A consumer electronics retailer has confirmed a data breach attempt to compromise the details of 5.9 million payment cards. On 13 June, Dixons Carphone released a notice disclosing its investigation into an instance of unauthorized data access. The company came across the suspicious activity while reviewing its systems and data. Subsequently, it contacted security experts to help determine what happened.