Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

#BigPictureCyber Town Hall With Glenn Gerstell, Senior Adviser to CSIS | 3/16/22 | NeoSystems

NeoSystems #BigPictureCyber Town Hall Series: Join NeoSystems’ Chief Information Security Officer, Ed Bassett, for our weekly #BigPictureCyber Town Hall designed for the Defense Industrial Base and GovCon community. Each session features special guests and offers an opportunity for attendees to ask questions regarding CMMC and cybersecurity. Topics covered include CMMC compliance requirements, cybersecurity news, how to prepare for CMMC certification, and the latest updates from the CMMC AB.

Create a Record

In this video, I will walk you through the creation of your first record. To begin, click the yellow Create New button and choose Record. You will notice a dropdown menu allows you to select the type of record you are creating. This allows users to create records of various template types, grouped into categories, each containing a unique collection of field types and functionality within the record. Examples of record types include: logins, payment cards, bank accounts, health insurance and many more. For more information on the Record Types feature, please see the video i’ve linked in the description below.

This Is the Reason Behind 70% Of Data Breaches

70% of the data breaches involve the negligence of a 3rd party. Let’s understand this with Target’s classic example. In 2013, they were using a contractor, Fazio, to do maintenance of their air conditioning systems. The hackers got into the Fazio systems and used it as a jumping pod to infiltrate and hack into Target’s infrastructure. Big companies like Audi and Volkswagen have also suffered such cyberattacks due to 3rd party negligence.

Identifying and Avoiding Malicious Packages

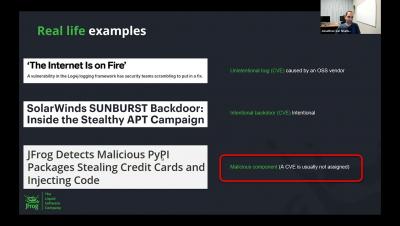
Securing your software supply chain is absolutely critical as attackers are getting more sophisticated in their ability to infect software at all stages of the development lifecycle. This webinar, hosted by JFrog Director of Threat Research Jonathan Sar Shalom, will be a technical showcase of the different types of malicious packages that are prevalent today in the PyPI (Python) and npm (Node.js) package repositories. All examples shown in the webinar will be based on real data and malicious packages that were identified and disclosed by the JFrog security research team.

Hello CISO - Episode 4: Employee Surveillance vs. Enterprise Security

How do you balance data collection at work with workers’ inalienable right to privacy? It's a fine line to walk, but if you always err on the side of employee privacy, it's hard to go wrong. In this episode of Hello CISO, Troy breaks down how to systematize that balance – and how to uncover the hidden costs of data collection. Hello CISO is a new series aimed at Chief Information Security Officers, IT security teams, and all other members of an organization responsible for maintaining the safety and integrity of the business and its operations.

Announcing Snyk free security for open source projects

Snyk announces expanded free offerings for open source project maintainers including unlimited scans across our platform and additional features. Snyk helps software-driven businesses develop fast and stay secure. Continuously find and fix vulnerabilities for npm, Maven, NuGet, RubyGems, PyPI and more.