Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Real-Time CMDB: The Data Your Automations Can Finally Trust

Most CMDBs are lying to you. The data looks clean, the dashboards look confident, and none of it reflects what's actually running in your environment right now. In this quick walkthrough, Steven Payne shows what happens when Tanium's real-time endpoint truth flows directly into ServiceNow's CMDB — no stale scans, no manual reconciliation, no guessing. Watch asset inventory, software, patch health, and vulnerability exposure snap into focus in real time, and see why "good enough" data is no longer good enough for the automations and AI your business is betting on.
What tasks should AI take over?

What part of your profession do you hope AI takes over? What should it never touch? Security practitioners and technology leaders landed in the same place: hand off the tedious work, and keep human judgment on anything that affects blast radius. That's the skills reckoning. As AI absorbs the repetitive work, the expertise that decides what an agent is allowed to reach becomes more valuable.

Autonomous Service Desk: A Ticket, Solved Before You Blink

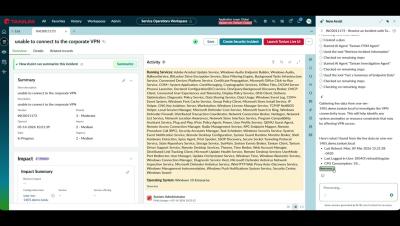
What if your service desk could solve a ticket before a human ever picked it up? Steven Payne walks through a live incident and shows ServiceNow's Now Assist doing the detective work in real time, pulling live Tanium endpoint data to pinpoint the root cause and draft the resolution, all in seconds. No log-diving, no remote sessions, no back-and-forth. Just a faster path from "ticket opened" to "issue resolved," with a person still firmly in control of the final call. This is what an autonomous service desk actually looks like in action — watch it happen.

"Speaking the Same Language" Tanium Atlas MCP Server: Tanium Tech Talks #169

Want to point your own AI at Tanium? The Atlas MCP Server makes that possible — governed, scoped, and available today. In this episode we cover: Tanium MCP - Available now (read-only) How to set up OAuth clients and how RBAC applies How to scope a single-purpose agent to one module, like Asset, using path-based tool filtering How to tell which tools consume Atlas AI credits - and which don't!

Autonomous Patch Management: Continuous, Closed-Loop Remediation

A critical vulnerability is discovered. Minutes later, it's patched — approved, scheduled, and deployed, with no one bouncing between systems to make it happen. In this video, Steven Payne shows how Tanium and ServiceNow close the gap between finding a problem and fixing it, turning a vulnerability into a governed change request and an executed patch deployment without a single manual hand-off. It's change management and endpoint remediation working as one motion instead of two disconnected jobs. If patch cycles have ever felt like a race against the clock, watch how much faster — and safer — that race can be.

Zlatko Unger has 35 minutes to stop AI from obeying poisoned emails (Live Tabletop Exercise)

You're the CISO at Larkfield Health, a 9,500-person health tech company. A little after 9:00 AM on a Tuesday, your Head of Detection forwards you a message from a security researcher you've never heard of. They say they've found a way to make Wingman—the AI assistant you rolled out company-wide six months ago—hand internal data to an outsider, and that a collection server that isn't theirs is already receiving it. Nothing in your own stack has made a sound.

Give access only when it's needed: Configuring Just-In-Time Application Allowlisting in MSP Central

Standing exceptions to your application control policy are exactly that—standing. Once you allow an app or lift a restriction, it usually stays open indefinitely, whether or not it's still needed. In this tutorial, we cover how to configure just-in-time (JIT) application access in MSP Central. Learn how to grant temporary, rule-based access to specific applications so users get what they need for a limited window, without leaving permanent access behind.

Falcon Next-Gen Identity Security: Agentic Identity Provider

CrowdStrike delivers the next evolution of the agentic SOC on the Falcon platform: coordinated teams of expert agents that investigate endpoint, identity, SaaS, cloud, and network domains simultaneously, converging on a single, evidence-backed verdict your team can trust.