Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What's Wrong With the Current State of Cyber Conferences

Cybersecurity conferences lose their value when the same vendor-led conversations keep repeating themselves. Community events such as BSides, Hack Glasgow and SteelCon offer a different model, where sponsors build credibility by supporting the community rather than throwing sales material at attendees.

From Cybersecurity to Cyber Resilience Understanding the Shift

From Cybersecurity to Cyber Resilience: Understanding the Shift Cybersecurity has evolved significantly over the past decade. Organizations have invested heavily in firewalls, endpoint protection, identity security, and other technologies, yet cyberattacks continue to grow in frequency and sophistication. So, what happens when prevention fails? The conversation is shifting from *“How do we prevent cyberattacks?”* to *“How do we continue operating when an attack succeeds?”*

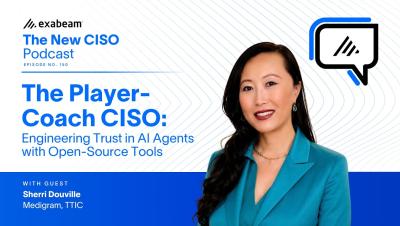
The New CISO Ep. 150 - Sherri Douville | Engineering Trust in AI Agents with Open-Source Tools

In this episode of The New CISO, host Steve Moore welcomes Sherri Douville for a conversation that sits outside the show's usual lane — less war story, more blueprint. Sherri works alongside CISOs rather than inside the role, and arrives with a pointed argument about what the job is becoming.

Episode 22 - The CTO's Case for AI: Fixing Bugs, Vibe Coding, and the Future of Dev Jobs

In this episode, host Richard Bejtlich sits down with Steve Smoot, Chief Technical Officer at Corelight, to explore how AI is reshaping the daily work of engineers and defenders alike. Steve traces his path from early employee to CTO and explains why the flexibility of Open NDR—where a simple ten-line Zeek or Spicy script can solve a customer's edge case without a full product release—remains a core advantage. The conversation digs into practical realities of working with large language models.