Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What Is AI Governance? A Practical Framework for Security Teams

The speed of AI integration is rapidly outpacing corporate governance capabilities. Generative AI is now embedded in development workflows and business applications, while agentic AI can make decisions and take actions with limited human intervention. That governance gap is becoming harder to ignore. Gartner predicts that more than 40% of agentic AI projects will be canceled by the end of 2027 because of escalating costs, unclear business value, or inadequate risk controls.
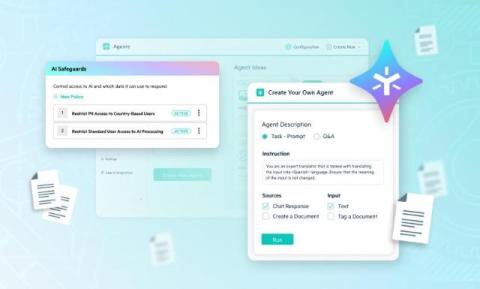
In AI Pilot Mode? Learn How to Scale AI Securely Without Shadow IT

You’ve seen the demos. You’ve run the pilots. Maybe you even deployed something that works, but is it scaling? Are your users utilizing it on a daily basis, or as intended? Or is it quietly gathering dust next to the last three tools that were supposed to change everything? Scaling AI the way most vendors describe it—connecting more tools and piping more data into more systems—doesn’t lead to progress or productivity. Rather, it results in additional risk.

CrowdStrike Expands Federal SOC Modernization Through CISA-Funded SIEMaaS

CISA has called SIEM-as-a-service (SIEMaaS) “the Rosetta Stone” for visibility for good reason. Federal defenders need to see what is happening across increasingly complex environments, understand what matters, and turn that context into action before an adversary achieves its objective.

Keeper Security Freshservice Workflow App Streamlines Vault and Privileged Access Request Process

Keeper Security, the leading zero-trust and zero-knowledge identity security and Privileged Access Management (PAM) platform, today announces a Freshservice Workflow integration that connects vault and privileged access requests to the ticketing systems IT and security teams already use. The integration lets agents fulfill Keeper vault access and approval requests – including Endpoint Privilege Manager and Cloud SSO device approvals – directly from a Freshservice ticket.

Reconciling an AI Risk Estimate Against What Truly Happened

A model produces a figure, an event happens, and somebody asks whether the figure was right. It is the obvious question and it has almost no published answer, because the comparison is harder than it looks. ‍ A single realized loss cannot falsify a distribution. If a model puts a one percent chance on exceeding a threshold and the threshold is exceeded, the one percent case occurred, which is what the model said would sometimes happen. ‍

The Cyber Risk Inputs That Move the Answer Most

A cyber loss model has dozens of inputs and every one of them can be argued about. Record counts, downtime costs, control effectiveness, secondary loss factors, event likelihoods. ‍ A few of them determine the answer and the rest barely move it. Knowing which is which tells you where estimation effort belongs, and more usefully which disagreements about the model are not worth having. ‍

PCI DSS Continuous Compliance: How to Keep Payment-Page Controls Working Between Audits

At the 2026 PCI SSC North America Community Meeting in Vancouver, continuous compliance was a recurring theme: how do organizations move beyond point-in-time validation and keep security controls working as their environments change? For payment-page security, that question is especially practical. Your last assessment captured your environment at a point in time. Since then, a release may have added a checkout dependency. A vendor may have updated its JavaScript. Marketing may have changed a tag.

Building for the Future: Why We're Doubling Down on Customer Experience at Brivo

One of the earliest business lessons I learned is the importance of taking exceptional care of customers. Focusing on a positive customer experience is a commitment and a business success strategy I’ve followed at Barracuda Networks, Eagle Eye Networks and now here at Brivo. Customers value a real person answering the phone, knowledgeable technical support, and professionals with regional and vertical market expertise.