Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Every New Compliance Framework Restarts the Same Fire Drill. It Doesn't Have To.

Every compliance audit starts the same way: Someone flags a deadline, the team scrambles to pull evidence, map controls, and prove that the policies running in production actually match what the framework requires. They make it through. They exhale. Six months later, a new framework arrives, and the fire drill starts all over again. Most teams walk away from an audit believing they are compliant.
Zlatko Unger has 35 minutes to stop AI from obeying poisoned emails (Live Tabletop Exercise)

You're the CISO at Larkfield Health, a 9,500-person health tech company. A little after 9:00 AM on a Tuesday, your Head of Detection forwards you a message from a security researcher you've never heard of. They say they've found a way to make Wingman—the AI assistant you rolled out company-wide six months ago—hand internal data to an outsider, and that a collection server that isn't theirs is already receiving it. Nothing in your own stack has made a sound.

Design tools around information, not APIs

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

CRA Compliance Gap Assessment: How to Identify Your Compliance Gaps

A CRA compliance gap assessment compares what your organization does with what Regulation (EU) 2024/2847 requires. It reviews each product and each role. It then produces a prioritized list of shortfalls. The list includes named owners, evidence pointers, and dates. It is not a conformity assessment. A conformity assessment decides whether a product may carry the CE marking. A gap assessment tells you whether you would survive one.

DIFC Regulation 10: AI system certification requirements orgs need to know

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Secure Data Sharing: Best Practices for Privacy and Compliance

Data sharing creates business value only when organizations can control where data goes, who can use it, and what happens after it leaves its original system. That becomes harder as businesses exchange customer records, financial information, healthcare data, and AI-ready datasets across employees, vendors, applications, and regions. The answer is not simply sending files through an encrypted channel.

Zombie work is biting CISOs

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

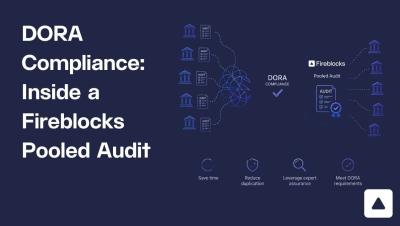
DORA Compliance: Inside a Fireblocks Pooled Audit

An internal auditor from Boerse Stuttgart Digital explains how a Fireblocks-hosted pooled audit helped meet DORA's third-party ICT requirements. Instead of every customer auditing Fireblocks one by one, the pooled audit community joined forces on a single common audit: shared scope, shared evidence, shared result. In this conversation, the pooled audit coordinator walks through how the community set the scope, why a pooled audit covers customer-specific requirements that a standard SOC 2 might miss, and how Fireblocks supported the process with subject matter experts, documentation, and on-site coordination.

How to define your third-party risk criteria

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.