Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

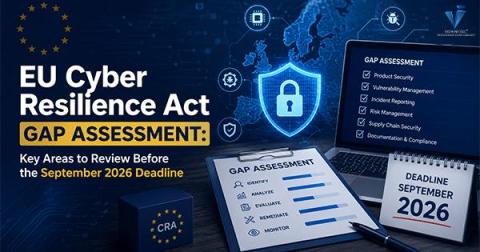
EU CRA Gap Assessment: Are You Ready for 2026?

Most compliance teams have filed the EU Cyber Resilience Act under “2027” — the date the regulation becomes fully applicable. That’s the wrong filing date. From 11 September 2026, manufacturers must already report actively exploited vulnerabilities and severe incidents affecting products with digital elements, more than a year before the rest of the regulation takes effect.

Jason Chan has 26 minutes to shut down a hacker hidden in plain sight (Live Tabletop Exercise)

What do you do when an attacker doesn’t break into your network, but simply walks in by turning your own multi-factor authentication against you? In this episode of The Tabletop, Jason Chan takes the hot seat and works the problem in real time.

Vanta's The Tabletop: Ep. 2 with Jason Chan

The attacker didn't break in. They logged in. In episode 2 of The Tabletop, Jason Chan (former VP of Security at Netflix) has 26 minutes to investigate an MFA fatigue attack that leads to a forgotten production script with hard-coded credentials... and no owner. His reaction says it all: "Archeology is part of our jobs… figuring out what this thing does.".

CrowdStrike Falcon Platform Helps Meet U.S. Government Mandates for CISA BOD-26-04

On June 10, 2026, the Cybersecurity and Infrastructure Security Agency (CISA) issued Binding Operational Directive 26-04, which transforms federal vulnerability management by shifting agencies from static CVSS-based patching to a dynamic, risk-based model. This supersedes BOD 19-02 and BOD 22-01. Agencies must now prioritize remediation using four key factors: public asset exposure, KEV catalog status, exploit automatability, and technical impact (partial vs. total control).

How to design a risk register: A guide for GRC practitioners

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Security Strategies That Help Minimize Data Breach Risks

Data compromises happen daily, creating massive headaches for companies of all sizes. Cyber criminals constantly find fresh entry points into modern networks. Smart business leaders focus on proactive defense methods to stay ahead of bad actors. Simple systemic upgrades can keep sensitive customer records safe from harm.

How to report risk to leadership and the board: A guide for security and GRC executives

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Beyond the Checkbox: How a Proactive Partnership Led to Turnkey Hazing Compliance

When we formed the global steering committee for our KnowBe4 Student Edition, our primary goal was to simply listen. That listening paid off during a pivotal conversation with a private research university in Florida. Their Chief Information Security Officer operates under a holistic mandate: to make the entire university ecosystem safer and more secure.

What Evidence Will Regulators Expect Under NIS2?

Being NIS2-ready is not just about implementing cybersecurity controls—you should also be prepared to demonstrate that appropriate cybersecurity risk-management measures are actually in place. In this video, we cover some of the key documentation and evidence organizations may need to maintain, including: Security policies and cybersecurity governance documentation Cybersecurity risk assessments and risk-management processes Incident response procedures Business continuity and crisis management plans Supply chain security practices Employee cybersecurity awareness and training activities.

How Professional IT Services Help Businesses Strengthen Security and Maintain Cybersecurity Compliance

Maintaining strong Cybersecurity Complianceis no longer something organizations can treat as an occasional task. Technology supports nearly every aspect of daily operations, from communication and collaboration to customer service and data management. When systems are not properly maintained, even a small security gap can lead to disruptions, data exposure, and unexpected costs. Taking a proactive approach to technology management helps reduce risk, improve reliability, and create a stronger foundation for long-term success.