Working with AWS to secure your data against attack
The content of this post is solely the responsibility of the author. AT&T does not adopt or endorse any of the views, positions, or information provided by the author in this article.


The content of this post is solely the responsibility of the author. AT&T does not adopt or endorse any of the views, positions, or information provided by the author in this article.
If you want to learn how to prevent a DDoS attack in your cloud environment by detecting the early signs of compromise associated with this threat, then this article should explain most of the best practices required to secure your cloud infrastructure. From January through July 2022, Sysdig Threat Research team implemented a global honeynet system that captured numerous breaches through multiple attack vectors.
Trustwave is proud to announce it has attained status as a Microsoft Cloud Solutions Partner for Security with a specialization in Threat Protection.
Hybrid working models have increasingly become the normal way of doing business. Employees are working from anywhere, users and their devices are moving on and off the office network, and many applications once hosted in data centers are now moving to public clouds or being replaced with software as a service (SaaS).
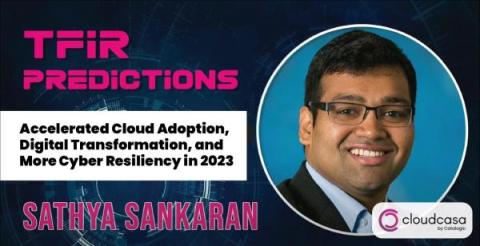
In this episode of 2023 Predictions, Sathya Sankaran, General Manager of CloudCasa by Catalogic, speaks with Swapnil Bhartiya on his insights into where he sees the industry heading in 2023. The pandemic resulted in the acceleration of cloud adoption and digital transformation and Sathya expects this momentum to continue in 2023 as well.
DevOps teams and developers can now bring the power of automated secrets detection and remediation to their Azure DevOps repositories.
In the first two blogs in this series, we discussed properly setting up IAM and avoiding direct internet access to AWS resources. In this blog, we’ll tackle encrypting AWS in transit and at rest.
Increased cloud adoption has introduced new security risks; organizations need to protect invaluable, sensitive data that can be accessed from anywhere. Traditional methods no longer suffice - today’s security operations teams must adopt innovative solutions and streamlined processes to effectively manage the increase in complexity and ensure mission-critical cloud loads are safeguarded.
Our most recent Cloud and Threat Report highlighted how threat actors abuse cloud services (with a special focus on cloud storage apps) to deliver malicious content (and yes, OneDrive leads the chart of the most exploited apps). To confirm that this trend will likely continue in 2023, researchers at Trend Micro have discovered an active campaign, launched by a threat actor named Earth Bogle.