Mailchimp
Not subscribed to OpsMatters Newsletter


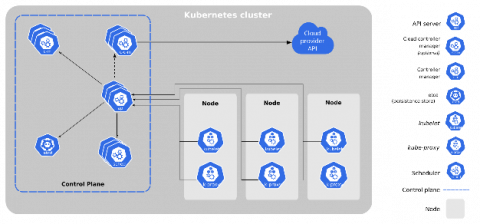
In Kubernetes, the task of scheduling pods to specific nodes in the cluster is handled by the kube-scheduler. The default behavior of this component is to filter nodes based on the resource requests and limits of each container in the created pod. Feasible nodes are then scored to find the best candidate for the pod placement. In many scenarios, scheduling pods based on resource constraints is a desired behavior.
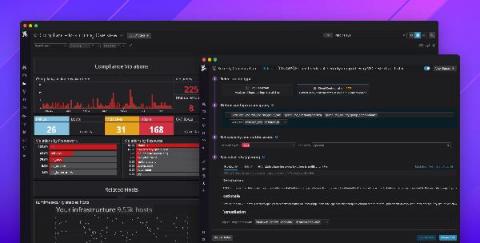
Governance, risk, and compliance (GRC) are major inhibitors for organizations moving to the cloud—and for good reason. Cloud environments are complex, and even a single misconfigured security group can result in a serious data breach. In fact, misconfigurations were the leading cause of cloud security breaches in 2020. This puts a lot of pressure on developer and operations teams to properly secure their services and maintain regulatory compliance.
This past year saw nearly a 300% increase in reported cybercrimes, according to the FBI’s Internet Crime Complaint Center (IC3). There has been a clear rise in threat volume and sophistication as many cybercriminals shift to techniques that can effectively evade detection and easily go after high-value targets. IoT devices are becoming a focus for threat actors, and threats related to credential harvesting and ransomware are also growing in number.
As the world is starting to move out of lockdown, businesses are moving some of their workforce back into the office environment. Whilst their focus may be on the logistics of this and making the office environment ‘Covid-Safe’ for their employees, they also need to be cognisant of the potential security challenges facing them.
We’re going to highlight the Top high severity CVEs found by Detectify. Thanks to the Crowdsource global community of handpicked ethical hackers, Detectify users get continuous access to the latest threat findings “from the streets” – even actively exploited vulnerabilities for which there aren’t yet any official vendor patches or updates.