Mailchimp
Not subscribed to OpsMatters Newsletter


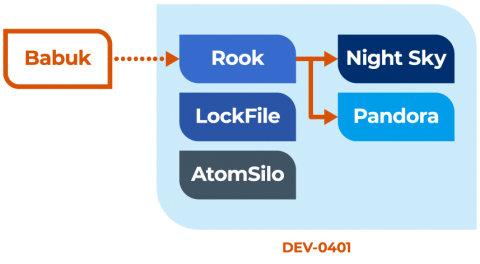
In a new threat briefing report, Vedere Labs analyzes the behavior of the Night Sky malware on two samples, presents a list of IoCs extracted from the analysis and discusses mitigation. The Night Sky ransomware was first reported on January 1, 2022. Victims were asked to contact the attackers to pay for the ransom. If the victims refused to pay, attackers threatened to expose their data on a leak site.
CrowdStrike recently demonstrated the power of the Falcon platform and its integrated approach to providing robust protection by exposing all attack tactics used as part of the MITRE Engenuity ATT&CK Enterprise Evaluation released in April 2022. The evaluation focused on emulating two of today’s most sophisticated Russian-based threat groups: WIZARD SPIDER and VOODOO BEAR (Sandworm Team).
Compliance should be an essential part of business operations, regardless of industry. Taking preventative measures to manage compliance and mitigate risk can feel like a hassle upfront, but it can save your organisation huge costs in the long run. Compliance violations can result in fines, penalties, lawsuits, loss of reputation, and more. However, your efforts should not stop at obtaining a compliance certificate, rather they should expand to accelerate your cybersecurity posture.
Telecommunication is the first, and most robust network ever invented. This may seem like a brazen and bold statement, but when examined closely, it is not the stuff of fantasy. Prior to the invention and development of the internet, what other way could a person pick up a device, and “dial” a few numbers and end up seamlessly connected to someone across the vast expanse of a countryside?
Is your team drowning in container vulnerability noise? Are you spending a lot of time figuring out where to focus resources on and still missing dangerous vulnerabilities? Know that you are not alone. Container environments revolutionized app development by enabling unprecedented velocity, but not without a price. The use of readily available container images of third-party and open-source code enabled much faster cycles, but also facilitated the introduction of vulnerabilities in the application.
Vulnerabilities are everywhere. Vetting, mitigating, and remediating them at scale is exhausting for security practitioners. Let’s keep in mind that no organization has the capacity to find and fix all vulnerabilities. The key is to understand what a vulnerability is, interpret the meanings of the CVSS score, and prioritize and effectively use resources within constrained time limits or delivery windows. Since 2016, new vulnerabilities reported each year have nearly tripled.