Mailchimp
Not subscribed to OpsMatters Newsletter


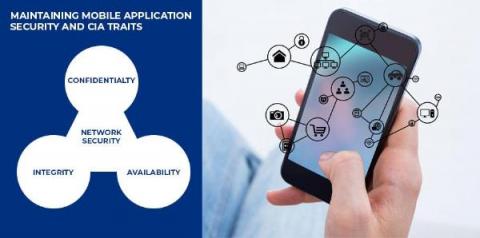
Nowadays, every business wants to reach out to a larger audience. And the best way for it is Mobile App Development. Whether someone is at work, at home, or somewhere outside, people frequently go through apps on their mobiles. Such apps collect data, store it and process it to provide reliable results. Indeed, our sensitive and confidential data is also getting into the same process. Hence, it makes a top priority to focus on mobile application security.
Vice Society, the cybercriminal gang responsible for the attack, is believed to have used internal login credentials leaked on the dark web to access LAUSD’s network and launch the ransomware attack. Twenty-three internal LAUSD credentials were leaked on the dark web leading up to the attack, with at least one set granting access to LAUSD’s Virtual Private Network (VPN).
The Uber data breach began with the purchase of stolen credentials belonging to an Uber employee from a dark web marketplace. The hacker tried to log into Uber’s network with these credentials but was unsuccessful because the account was protected by MFA. To overcome this security barrier, the hacker contacted the employee and, while pretending to be a member of Uber’s security team, asked them to accept the MFA push notification sent to their phone.
Migrating to the Cloud brings many advantages for companies. First of all, they reduce their operating costs by almost 40%. They also increase their agility, reduce the maintenance time of traditional IT infrastructures, and gain flexibility and scalability. However, as the number of workloads deployed in the Cloud grows, more and more organizations are struggling to keep pace with security requirements.
The increasing use of cell phones has automatically led to unimaginable height of sharing of personal information online. Most routine actions, from providing information over the phone to opening a bank account to placing food orders, may now be accomplished from the convenience of your own home. While the telecom sector has enabled remote procedures, it has also hastened the spread of identity fraud and financial schemes.
A selection of this week’s more interesting vulnerability disclosures and cyber security news. For a daily selection see our twitter feed at #ionCube24. Normally the articles I share come as some surprise. This week I don’t think any one of them meets that criteria…. So let’s start with the first non-surprise then… With silly shopping season ahead of us it comes are utterly no surprise that eCom stores are under attack.
Evolution of the SOC – From the Dark Ages to Enlightenment, shifting to an agile threat informed cyber defense program How important is the Security Operations Center (SOC) to a business and a security leader's overall success? The answer is a bit cloudier than one would believe, given the length of time the SOC has been part of our security program lexicon.
When it comes to security in AWS, there is the shared responsibility model for AWS services, which is divided into AWS responsibility ‘security of the cloud’ and customer responsibility ‘security in the cloud’. For more detail on this please check the shared-responsibility-model. Figure 1: AWS Shared Responsibility Model Source: shared-responsibility-model.
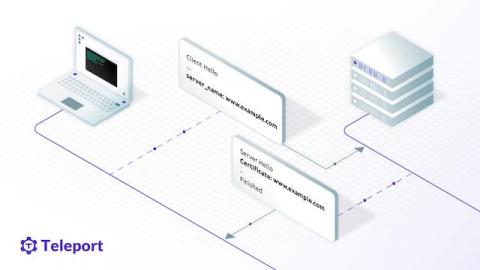
In Teleport 8, we introduced the TLS Routing feature that can multiplex all client connections on a single TLS/SSL port. Recently we've added support for TLS Routing for Database Access when Teleport is deployed behind an AWS Application Load Balancer (ALB). In this article, we will take a deep look at the problem with Teleport behind an ALB and how we solved it.