Mailchimp
Not subscribed to OpsMatters Newsletter


The Federal Information Processing Standard (FIPS) 140-3, is a collection of standards released by the United States government to examine cryptography modules. It explains how to design, develop, and run a cryptography module. The National Institute of Standards and Technology (NIST) and Communications Security Establishment (CSE) created FIPS 140-3 to safeguard critical, unclassified information.
Attack surfaces are a fundamental concept within information security. However, attack surfaces can be constituted of different things. For example, some formulations of an attack surface include not just software and hardware, but the people using them. In this post, we’re going to cover four common types of attack surface, discuss how you should think about the risks associated with each type, and best practices for addressing these risks.
Major companies have suffered serious data breaches this week, and even the city of Dallas, Texas, was hacked and damaged by data attacks that could expose a significant number of people, making it clear that everyone is at risk when it comes to identity theft and data attacks specifically. Huge mental health organizations like Brightline and Mcpherson Hospital exposed confidential patient data, and even the Metropolitan Opera House in New York City was the target of a breach attack this week.
Carvin Software is a massive company based in Gilbert, Arizona. The company creates specialized software solutions for business owners and individuals throughout the country. Carvin specializes in construction software but offers staffing solutions and other types of software services as well. A large variety of companies work with this organization, including Apple Staffing, Ace Personnel, Labor Force, and more.
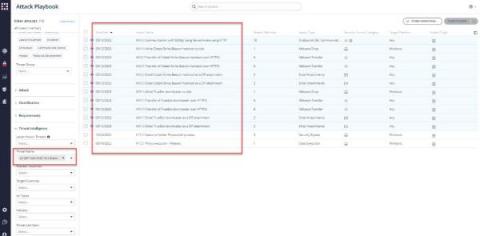
On May 11th, the Cybersecurity and Infrastructure Security Agency (CISA) and the Federal Bureau of Investigation (FBI) released an advisory highlighting the active malicious exploitation of CVE-2023-27350 in PaperCut MF and PaperCut NG software by a threat actors including one known as the Bl00dy Ransomware Gang. The US-CERT Alert (AA23-131A) Malicious Actors Exploit CVE-2023-27350 in PaperCut MF and NG includes detailed information about this investigation (along with attacker TTPs and IOCs).