A secrets vault controls the credentials you manage. Detection finds the ones that escaped. Here are six reasons mature secrets management programs need both.
You might treat a centralized vault as the authoritative source for every secret, but secrets can quietly fall out of sync as they get copied into cloud secret stores, CI/CD pipelines and running workloads. This is referred to as secrets configuration drift, and it can leave outdated or standing credentials, API keys and other secrets active for longer than intended.
Your security stack is a set of specialists, each guarding one territory. Exposed credentials don't respect the boundaries between them, and 64% of the ones found valid in 2022 were still valid four years later.
A new Mini Shai-Hulud wave hit keyv and 800+ npm packages. The malware now scans 469 secret locations, including AI agents, crypto wallets, and CI/CD tools.
Credential harvesting is how attackers collect valid secrets at scale. See how it works, why developer machines are a prime target, and how to find them first.
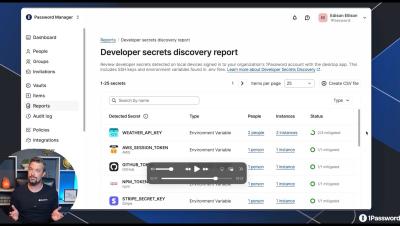
Your.env file has your database password, your AWS keys, and your Stripe secret, all in plaintext, sitting on your laptop. 1Password Developer Watchtower finds it, 1Password Environments secures it, and you keep shipping. See how 1Password discovers plaintext developer credentials, imports them into an encrypted environment, and mounts a virtual protected.env, with no workflow disruption for developers and full fleet visibility for security teams.
Learn how to measure time to revoke for exposed credentials using validation and invalidation timestamps, remediation SLAs, and CISO reporting metrics.
Developers, how are you managing your secrets? Keeper Security’s Universal Secrets Sync automatically distributes credentials and secrets stored in Keeper to external secrets managers and cloud platforms, including AWS Secrets Manager, Azure Key Vault and Google Cloud Secret Manager.