Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

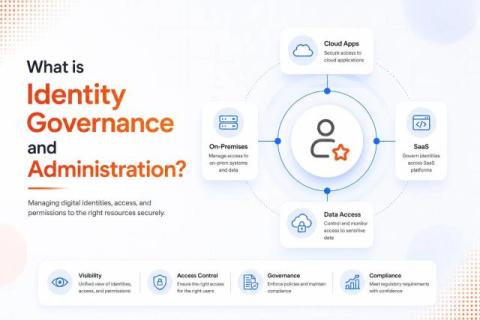
What is Identity Governance and Administration (IGA)?

Enterprises today manage thousands of identities across employees, contractors, applications, APIs, and machine-driven systems. In most environments, identities have become the primary security boundary, yet access remains fragmented, overprovisioned, and difficult to track. According to IBM's X-Force Threat Intelligence Index, identity-based attacks now account for nearly one-third of all intrusions, highlighting how identity has become one of the most targeted layers in modern cybersecurity.
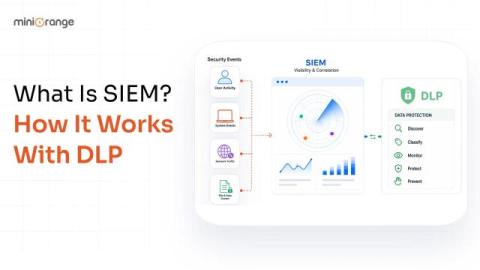
What Is SIEM? How It Works With DLP to Detect Data Threats

Most security teams don’t lose the fight against data breaches because they lack tools. They lose because their tools don’t talk to each other. This is exactly the loophole that SIEM and DLP were built to close, together. Security information and event management gives you visibility into what’s happening across your entire environment. At the same time, data loss prevention gives you the control to stop sensitive information from leaving in the first place.

One Identity CEO talks winning CISO board pitch & identity fabric

Breaches will impact an organization greatly, regardless of industry or your role in it, and Larry Chinski, VP of enterprise strategy, caught up with CEO Praerit Garg to explore the challenges facing CISOs in trying to communicate this fact. Tune in for insights on learning to speak the ROI-focused language of the board when pitching a security budget. And keep watching for a discussion on the benefits behind a comprehensive identity fabric for your identity security.

Session on AirGapped AI - Adopt AI Privately and Securely, AI Trends from Around the World at CyBe

In this session at CyBe AI Summit 2026, NIMHANS Convention Centre in Bengaluru, our Founder & CEO Mr. Anirban Mukherji discussed current AI trends, geopolitical and sovereignty risks tied to frontier LLMs, and practical implementations for India. He addressed how AI-driven automation like delivery robots and drones can disrupt jobs, why governments and defense agencies require air-gapped or on-prem solutions, and how cost and restricted access to frontier models create inequity in AI adoption.

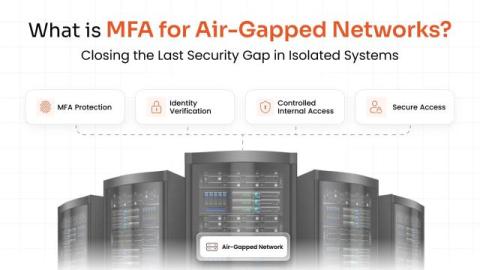
What Is MFA for Air-Gapped Networks? Closing the Last Security Gap in Isolated Systems

Air-gapped networks are supposed to be untouchable. No internet connection, no remote pathway, no way in for an attacker sitting halfway across the world. But ask any security team that has actually run one of these environments, and you'll hear a different story. Air gaps stop remote attacks cold. But they do almost nothing to stop a stolen password, a careless USB stick, or an insider with too much trust and too little oversight. That's the gap, and Multi-Factor Authentication (MFA) is here to fill it.

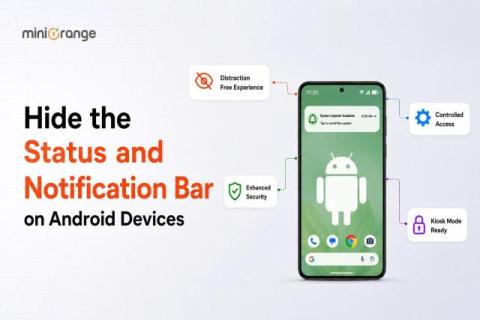
How to Hide the Status Bar and the Notification Bar on Android Devices?

Android devices are designed for flexibility. Employees can check notifications, adjust connectivity, open settings, and move between apps with a few taps. That flexibility works well for personal use, but it can introduce distractions, security gaps, and usability issues when a device is dedicated to business tasks.

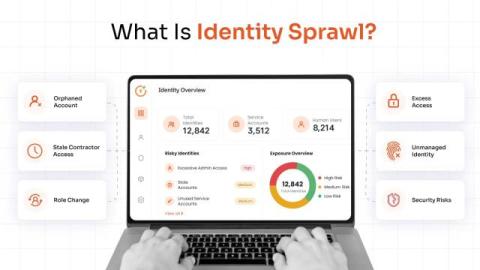
Identity Sprawl: Risks, Causes, and Best Practices for Enterprise Identity Management

An employee leaves the company, but their SaaS account remains active. A contractor still has access to a project workspace months after the contract ends. Someone changes departments and keeps permissions from their previous role. Meanwhile, IT is managing identities, human and non-human across multiple directories, cloud platforms, SaaS applications, and third-party tools. Individually, these accounts may seem insignificant.

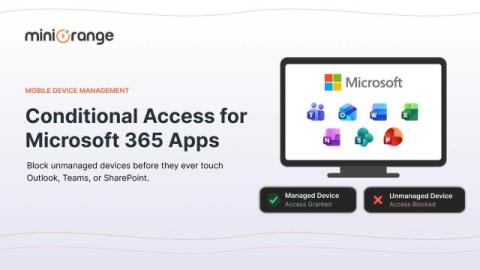
How Conditional Access Protects Microsoft 365 Apps From Unmanaged Devices

Your sales representative logged into Outlook from a coffee shop laptop that isn't enrolled, isn't encrypted, and hasn't seen a security patch in eight months. Should Microsoft 365 let that sign-in through just because the password was correct? That single question is why conditional access exists. Passwords tell you who someone claims to be. They say nothing about whether the device behind that login is safe to trust with your company's email, SharePoint files, or Teams chats.

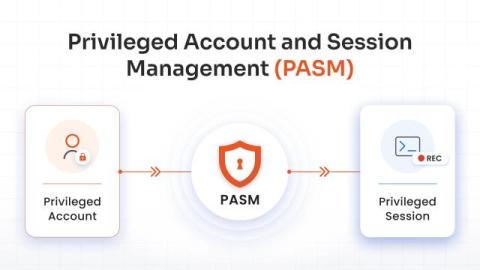
Privileged Account and Session Management (PASM) Explained

Privileged accounts have elevated access that can be used to rewrite system configurations, alter sensitive databases, create new admin users, and exfiltrate confidential customer data. This makes them attractive targets for attackers and risky when poorly managed. Basic passwords and network firewalls aren’t enough to protect them. You need to monitor them continuously. This is where Privileged Account and Session Management (PASM) becomes essential.

Falcon Next-Gen Identity Security: Agentic Identity Provider

CrowdStrike delivers the next evolution of the agentic SOC on the Falcon platform: coordinated teams of expert agents that investigate endpoint, identity, SaaS, cloud, and network domains simultaneously, converging on a single, evidence-backed verdict your team can trust.