Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

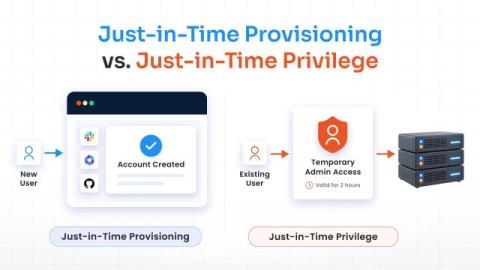
Just-in-Time Provisioning vs. Just-in-Time Privilege: What's the Difference?

Just-in-Time Provisioning and Just-in-Time Privilege sound almost identical, but they solve different identity management challenges. Let’s say a new software engineer joins your team. They need access to Slack, Jira, GitHub, and other essential apps. Instead of having an IT admin create their account manually, the application creates the account when the employee signs in through your Identity Provider (IdP). That is JIT provisioning.

AI Agents Are Forcing Us to Rethink Identity

Since joining BlueVoyant in May, I’ve spent my first 100 days listening. I've had conversations with nearly 50 customers and partners across industries and geographies, as well as the broader security industry, engaging with leaders at Black Hat last month. What I heard reinforced something I believe strongly: the security challenges organizations face today are changing faster than the traditional enterprise security model was designed to handle.

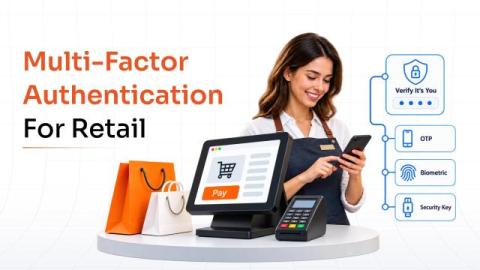
MFA for Retail: Smarter Authentication for Stores, E-commerce & Employees

A refund is an authentication event, so are a POS login, a loyalty-account change, and a technician connecting to a store remotely. Retailers have traditionally treated these moments as separate access problems, but they share the same underlying question: how much confidence should the business require before allowing an action to proceed?

User Access Management: Process, Controls, and Benefits Explained

Access sprawl is quiet. For example, a contractor's admin rights outlive the project by eight months, or an account sits open for weeks after someone switches teams. And in most cases, nobody catches access sprawl until an audit or a breach forces the question. User access management (UAM) is the discipline that catches this. It decides who gets access to what, why they get it, how that access is approved, how it changes over time, and when it gets pulled.

Beyond the Login Screen: Why Qualified Electronic Signatures Belong in Identity Security

For years, identity security was mostly discussed as an access problem. Can the right person log in? Is multi-factor authentication enabled? Are privileged accounts protected? Can stolen credentials be used from an unknown device? Those questions still matter. But they describe only the beginning of a digital transaction.

SSH Session Monitoring: How to Monitor, Record & Audit SSH Sessions

Secure Shell (SSH) gives you direct access to critical servers, databases, and cloud infrastructure. Once a privileged user connects through SSH, they hold extensive control over that system. They can alter core configurations, run terminal scripts, move files, or delete production databases in seconds. If you lack visibility into privileged actions, it can be risky. If a credential gets stolen or an insider goes rogue, traditional firewalls won’t be enough.

How Is AI Transforming Identity and Access Management?

Traditional Identity and Access Management (IAM) relies on authentication methods, predefined roles, and access policies to control who can access business applications and data. These controls remain essential, but they do not always provide enough context to identify unusual behavior or changing access risks. AI in Identity and Access Management (IAM) adds another layer of intelligence by analyzing login context, user behavior, device information, access patterns, and identity activity.

MFA for Telecommunications: Securing Networks, Admins, and Customer Accounts

A single telecom login is one of the most dangerous keys in existence. Behind it sit subscriber identities, billing systems, and the network backbone every other industry depends on. In April 2025, SK Telecom admitted attackers had stolen authentication records tied to its USIM cards, affecting 27 million subscribers, with malware present for years before discovery. Weeks earlier, the FBI warned of a campaign using AI-generated voice and text to trick targets into handing over account access.