Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Securing Kubernetes using Egress Access Controls

A majority of existing workloads are non-Kubernetes, and for the platform teams involved, this creates challenges because the cluster will need to be securely connected to those resources. Calico Enterprise includes several features that enable fine-grained access controls between your microservices and databases, cloud services, APIs, and other applications that may be protected behind a firewall. There are different approaches to managing Kubernetes egress access, depending on your needs and where you want the control point to be

Your team is running containers, but are they secure?

Organizations are modernizing IT infrastructure, restructuring teams, and accelerating application delivery with containers and Kubernetes. As with any technology, organizations are at various places within their journey. However, according to Gartner, more than 75% of global organizations will be running containerized apps in production by 2022. Chances are your team is using containers for some applications.

Deploying Calico in Your On-prem Kubernetes Cluster: Networking and Security Considerations

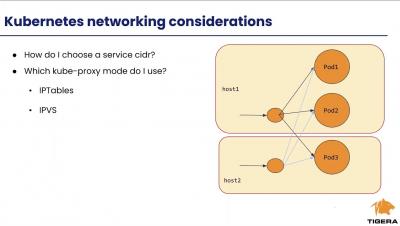
If you are deploying Kubernetes on-premises in your datacenter, this is a talk and demo you won’t want to miss. Networking and security might not be the first things that come to mind, but without some understanding of the networking and security decisions you’ll need to make, and the right options for your environment, you’re likely to get stuck or make the wrong assumptions. These may limit your ability to scale or integrate with the rest of the datacenter network.

CI/CD With Veracode Docker Images

On November 19, Veracode published new, official Docker images for use in continuous integration pipelines. The images, which provide access to Pipeline Scan, Policy (or Sandbox) scans, and the ability to access Veracode APIs via the Java API Wrapper or via HTTPie with the Veracode API Signing tool, make it easy to include the current version of Veracode tools in your automation workflow.

How to secure a Kubernetes cluster

More and more organizations are adopting Kubernetes, but they’re encountering security challenges along the way. In the fall 2020 edition of its “State of Container and Kubernetes Security” report, for instance, StackRox found that nearly 91% of surveyed organizations had adopted Kubernetes, with a majority (75%) of participants revealing that they had deployed the container orchestration platform into their production environments.

Security, compliance, and visibility for Amazon EKS-D

Today AWS unveiled the Amazon EKS Distro (EKS-D) and Sysdig is excited to deliver support for the new Kubernetes distribution with our Secure DevOps solutions. Wherever you choose to run EKS-D to run container applications, Sysdig can also be used to detect and respond to runtime threats, continuously and validate compliance, as well as monitor and troubleshoot.

Data Protection in the Age of Kubernetes

Software containers are at the heart of cloud-native business transformation initiatives. Containers are a natural evolution from virtual machines to a more granular and portable application environment in clouds. They are designed to support rapid development and deployment of cloud-native applications in what is called a DevOps model, a set of practices that combines software development and IT operations.

Introducing CloudCasa: Kubernetes Backup and Disaster Recovery

Introducing CloudCasa – A Smart Home for Protecting Your Cloud Data. CloudCasa is a Kubernetes (K8s) native and cloud native Software-as-a-Service (SaaS) solution that supports backup of Kubernetes clusters. CloudCasa offers a free service to backup your metadata and resources data to S3 and orchestrate Container Storage Interface (CSI) snapshots on your Kubernetes clusters.

Securing Kubernetes clusters with Sysdig and Red Hat Advanced Cluster Management

In this blog, we introduce the new integration between Sysdig Secure and Red Hat® Advanced Cluster Management for Kubernetes that protects containers, Kubernetes, and cloud infrastructure with out-of-the-box policies based on the Falco open-source runtime security project. Organizations are quickly growing their Kubernetes footprint and need ways to achieve consistent management and security across clusters.