Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Is prevention essentially a solved problem?

Stopping new security issues in agent-generated code from being deployed is, architecturally, a solved problem. Prevention is the act of keeping a new vulnerability in code from reaching production at any point in the development and release process, including but not limited to preventing its introduction in a feature branch.
Looking Ahead from VMware Explore

Our time at VMware Explore reinforced what we believe and continue to see across the industry: VMware remains the leader in virtualization and cloud infrastructure. VMware Cloud Foundation (VCF) continues to push the envelope with a powerful set of built-in capabilities that help organizations build, operate, and secure modern environments. Time and again, we saw how these capabilities are enabling businesses to simplify complexity and operate with greater confidence.

Gamepad Mapper vs Controller Remapper: What's the Difference?

PC gamers often come across terms such as gamepad mapper, controller remapper, and controller mapping software. These terms can sound interchangeable, and in many cases they are used to describe similar tools. However, there are some differences in how these applications are typically used. Understanding the terminology can help you choose the right solution for your setup. Whether you simply want to change a few buttons or build a completely customized control scheme, the important thing is to understand what the software can actually do.

How Wearable Technology Turns Everyday Movement into Meaningful Data

A walk to the shops rarely feels worth recording. Neither does climbing stairs with laundry or taking a longer route home. Yet these ordinary movements make up part of daily activity. Wearable technology gives those scattered moments a visible record, creating an opportunity to notice routines that memory alone might overlook.

Securing AI API Keys From Development to Production

An AI feature can reach production before anyone has decided who owns its credentials. A developer creates an API key for a prototype, a colleague copies it into a background worker, and a troubleshooting session puts the same value into a support ticket. The application works, but the team can no longer say exactly where its access begins or ends.

Seedance 2.5: AI Video Is Learning to Handle What Happens Between the Shots

Turning a photograph into moving footage has become familiar. The details that make people keep watching usually come from the relationships inside the frame: why a character turns at that moment, why the product appears there, why the music lands on that beat, and how the camera carries the viewer toward what comes next.

uMobix and the Missing Middle: What Happens Between "Everything Is Fine" and a Real Online Problem

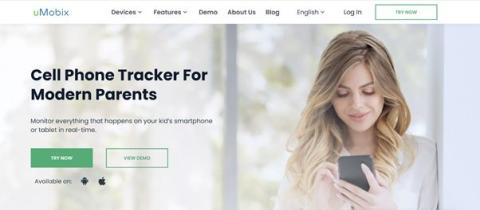
Most parenting advice about online safety talks in two modes: everything is fine, or something is seriously wrong. What rarely gets discussed is the long, ambiguous stretch in between, where a little secrecy, an odd new habit, or a slightly different mood doesn't clearly belong to either category. That missing middle is where most real situations actually live, and it's exactly where parents feel least equipped to act, since nothing they've read prepares them for something that isn't clearly one thing or the other.

Posture Management: A Modern Approach to Building Security That Holds

Security posture is one of the most used yet misunderstood concepts in cybersecurity. For some, it means being audit-ready. For others, it’s shorthand for how many tools are deployed across endpoints, identities, and cloud environments. But in practice, posture is something deeper. It’s the ability of your environment to withstand real-world threats, not just meet compliance requirements. Strong posture doesn’t just reflect what’s present.

9,000+ Incident Response Investigations Later: The 11 Essential Cybersecurity Controls

Organizations with mature security programs still get breached. Teams that pass audits still find themselves responding to ransomware, Business Email Compromise (BEC), and credential theft. The controls that satisfy an audit requirement and the controls that significantly reduce the likelihood, impact, and cost of an intrusion are often not the same.

CISO Risk Intel Brief: Exploited Control Planes, Not Patch Volume, Define Residual Risk

This executive intelligence briefing covers from the past week (2–9 September 2026) and the past month (approximately 10 August – 9 September 2026). CISOs, start here: do not open a 974-row spreadsheet. That queue is the failure mode. This week’s material risk sits in four places you can name before noon.