Agentless bot management provider ranked among top players in Analyst Report Manchester, 12th April, 2022 – Netacea, the bot detection and mitigation specialist, today announced it has received the highest score in the Bot Detection criterion in The Forrester Wave™: Bot Management, Q2 2022 report.
According to the 2021 Devo SOC Performance ReportTM — which is based on the results of a survey of more than 1,000 security practitioners — having an understaffed SOC or constant turnover of security talent can cripple an organization’s security posture. Let’s look at some of the root causes that can lead to these two interconnected problems.
Prof. Avishai Wool, AlgoSec co-founder and CTO, stresses the importance of getting the often-overlooked function of managing network objects right, particularly in hybrid or multi-vendor environments.
In December 2020, Microsoft came forward with details regarding what is now being considered the most extensive, severe cyberattack in history—the NOBELIUM attack. This shocking security breach by NOBELIUM, a group of Russian hackers, brought the cybersecurity world to a standstill with its well-planned and well-executed hacking. It compromised several organizations through a supply chain attack.
It is becoming increasingly difficult to guarantee a safe boundary for your sensitive data. As work-from-anywhere cements, employees are now collaborating freely with each other, with contractors and with partners. But this freedom to collaborate more broadly also means information is being shared among devices, applications and networks that your organization doesn't necessarily have control over.
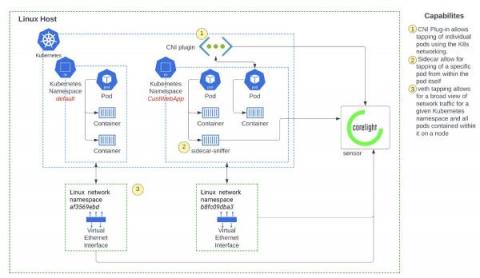
Network monitoring solutions can overcome the security visibility blind spots in Kubernetes environments, by providing a source of truth for SOC analysts. Container security solutions broadly span the spectrum of (a) prevention - securing the container image and ensuring the right policies are in place during runtime and (b) detection - monitoring runtime events for threat detection and investigation.