Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

No more blind trust: How risk-based authentication strengthens identity security

Traditional digital authentication methods have allowed users to enter and IT infrastructure if they hold the right key. Username and password alone provided limited context around the authenticity of the access attempt. But today, the person with the credentials may not claim who they are.
Featured Post

One View, More Control: The Strategic Value of an Integrated IT Operating Model

Businesses are managing increasingly complex technology environments. Infrastructure, cloud, data protection, cybersecurity and continuity services all play a critical role in keeping organisations productive, resilient and ready to grow. At the same time, technology leaders are under pressure to improve efficiency, control costs and demonstrate clear value from every investment. In this environment, the challenge is not just choosing the right technology, but creating an operating model that gives the business control without adding unnecessary complexity.

5 best GRC software solutions for enterprise teams in 2026

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

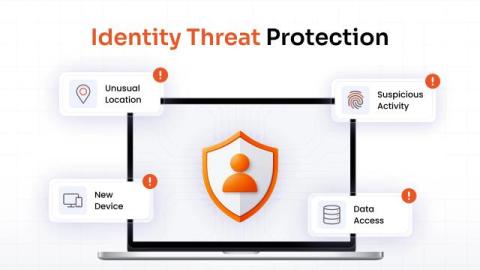
Identity Threat Protection: What It Is, How It Works, and Best Practices

Identity Threat Protection (ITP) helps organizations detect and respond to threats by monitoring identity activity, analyzing risk signals, and applying security controls. This guide covers what identity threat protection is, how it works, its key capabilities, and the best practices organizations can follow to protect identities.

Why Privileged Access Management Is Essential for GCC Organizations

Gulf Cooperation Council (GCC) enterprises are rapidly adopting cloud technologies and rolling out massive AI initiatives, with many moving from pilots into production. More systems now connect through APIs. That progress also expands your privileged attack surface. When you give users unchecked access to critical systems, even one compromised identity can bring everything down.

Fine-Tuning Is Not What Reclassifies an AI Deployer

The concern about fine-tuning is that it quietly converts a deployer into a provider, pulling in conformity assessment, technical documentation and a quality management system nobody budgeted for. ‍ The concern is misdirected. Fine-tuning is among the least likely routes to reclassification, and the route almost nobody worries about requires no training compute at all. ‍

Uncovering indirect attack paths to virtualized domain controllers in Azure

Within Netwrix Security Research, we were helping a customer with an Entra ID assessment and knew they'd already done AD tiering on-prem. We also knew they had domain controllers virtualized in Azure, but it was hard to tell which Windows Server was actually a DC. We figured out that Azure Run Command lets you run commands as SYSTEM, so we used that to do reconnaissance and identify the DCs.