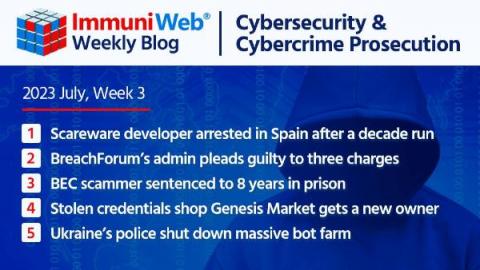
Scareware Scammer Arrested In Spain After 10 Years On The Run
Read also: BreachForum’s admin pleads guilty to three charges, Genesis Market gets a new owner, and more.


Read also: BreachForum’s admin pleads guilty to three charges, Genesis Market gets a new owner, and more.
Human error is a major contributing factor to company data breaches. More than 340 million people may already have been affected by a data breach in the first four months of 2023. With cybercrime rates soaring around the world, it’s clearly an area where investment and expertise are required.
We're all familiar with tech support scams - where the unwary are tricked into granting remote access to their computers by fraudsters, in the belief that the "tech support person" will fix a non-existent "problem" (such as a "virus infection") or make a refund after claiming that there has been fraudulent activity detected on an account.
A selection of this week’s more interesting vulnerability disclosures and cyber security news. A basic a security failure. Pretty damaging to them as well as their users…
Six months ago, the question, “Which is your preferred AI?” would have sounded ridiculous. Today, a day doesn’t go by without hearing about “ChatGPT” or “Bard.” LLMs (Large Language Models) have been the main topic of discussions ever since the introduction of ChatGPT. So, which is the best LLM? The answer may be found in a surprising source – the dark web. Threat actors have been debating and arguing as to which LLM best fits their specific needs.
Should we be using multiple public cloud providers? As organizations continue to migrate applications and workloads to public cloud platforms, they often face the tough decision of sticking with a single provider or embracing multiple clouds. Using multiple cloud providers promises a variety of benefits including the ability to minimize vendor lock-in, leverage best-of-breed services, achieve cost advantages, and comply with data sovereignty rules.
DeepScan is an innovative product that uses Artificial Intelligence (AI) and Machine Learning (ML) to recognize and extract data from physical documents like images or PDFs. It’s been a game-changer in the field of invoice processing.