Mailchimp
Not subscribed to OpsMatters Newsletter


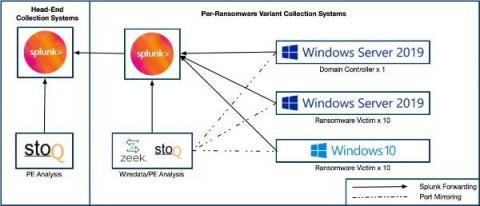
Do you feel like every other cybersecurity news story mentioned ransomware in 2021? Does it feel like you can’t turn on a cybersecurity podcast and not hear the “R” word? We feel the same way, and as a cybersecurity vendor, we felt that we should also contribute to the noise. :-) But we did want to try and do something different.
“In its current CWS offering, the vendor has great CSPM capabilities for Azure, including detecting overprivileged admins and enforcing storage least privilege and encryption, virtual machine, and network policy controls.” – The Forrester Wave™: Cloud Workload Security, Q1 2022 CrowdStrike is excited to announce we have been named a “Strong Performer” in The Forrester Wave:™ Cloud Workload Security, Q1 2022.
In an effort to stay ahead of improvements in automated detections and preventions, adversary groups continually look to new tactics, techniques and procedures (TTPs), and new tooling to progress their mission objectives. One group — known as BlackCat/ALPHV — has taken the sophisticated approach of developing their tooling from the ground up, using newer, more secure languages like Rust and highly customized configuration options per victim.
Our VP for Data Ethics & Governance, Sophie Chase-Borthwick, was recently part of a panel – the PICCASO Special Interest Group. Sophie joined William Malcolm (Privacy Legal Director at Google), Radha Gohil (Data Ethics Strategy Lead at Shell), and Anne Woodley (Security Specialist at Microsoft) in untangling what data ethics actually means and how best to support it. Here we look at this in more detail.
I’m not big on acronyms or buzzwords. Like many executives, my eyes glaze over when I’m being prospected with an alphabet soup of technology terms I supposedly “need” to care about. So why, then, does the title of this article include Security Service Edge (SSE), Secure Access Service Edge (SASE), and Zero Trust? Despite our justified disdain for acronyms, the ideas behind these terms hold genuine importance for business leaders.
Trustwave is actively tracking the threat of Lapsus$ for our clients. We encourage all organizations, especially those part of the digital supply chain, to remain vigilant and ensure that cyber best practices are implemented. We are actively investigating all unusual login behaviors for clients that use Okta. For more information on the Okta incident, please visit their blog. Trustwave does not use Okta. Actionable security recommendations for organizations can be found below.