Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Stop Guessing. Find the Root Cause with Cato DEM.

When a user says, “the application is slow,” IT has to answer a much harder question: where did the problem actually begin? The issue could be on the endpoint, local network, ISP, the network path, enterprise infrastructure, or application provider itself. That investigation often takes time because teams have to reproduce intermittent problems, collect evidence from separate tools, and hand cases between endpoint, network, and application owners.
Building Mobile Apps That Scale: A Business Leader's Perspective

Most mobile apps are built for the business as it exists on launch day. The trouble starts when the business keeps growing. A customer app that worked well for 5,000 users begins to slow down at 50,000. An ordering app that served one region struggles when the company expands nationwide. New features take months instead of weeks, and every release feels risky. These are not signs of bad luck. They are signs of an application that was never designed to grow.

Building a Network Appliance on RK3588? How Kiwi Pi 5 Pro and Orange Pi 5 Plus Compare

For gateways, edge nodes and remote monitoring boxes, the number of network paths a board offers often matters more than its benchmark score. Two popular RK3588 boards take noticeably different positions on that question.

How to Pick a Secure Minecraft Server Host

Most people pick a host on price and RAM. Security barely comes up, right up until somebody's world gets wiped. It happens more than you'd think. Weak panel logins, open ports, no backups, admin passwords that were never changed. None of that shows up on a sales page. Alright, so before you go picking a host, there are a few things worth checking. Some stuff looks great on the website but turns out pretty useless once you've actually paid. And yeah, there are a couple of things I'd stay away from completely.

5 PQC Remediation Platforms That Take Programs From Discovery to Done

Post-quantum cryptography programs can no longer stop at finding vulnerable encryption. Discovery is necessary, but discovery alone does not make an enterprise quantum-safe. Organizations still need to determine which cryptographic risks matter most, decide what should be migrated first, coordinate changes across application and infrastructure owners, select appropriate remediation strategies, validate that each fix worked, and maintain visibility as cryptography continues to change.

Modern Standards of LinkedIn Marketing for Sales Team Efficiency

LinkedIn has become the core B2B sales channel, but approaches to outreach have evolved. Generic mass messaging no longer yields results. Success now depends on precision, warm engagement, and safety. Sales teams require structured role distribution, multi-step personalization, and specialized tools to prevent duplicate outreach and account bans. To scale effectively without risking profiles, companies use reliable LinkedIn automation software for sales teams. Solutions like Linked Helper offer local desktop execution, smart human-like action imitation, and centralized workspaces.
Featured Post

Why Smarter Factories Can Create Greater Operational Risk

The manufacturing industry has undergone a remarkable transition. Factories that once relied on largely isolated systems and manual processes have evolved into highly connected environments, where cloud platforms, industrial technologies, data and third-party services work together to keep production moving. The benefits are clear, with greater connectivity helping manufacturers to increase efficiency and productivity, while better access to data gives teams the insights that they need to optimise operations and make faster, more informed decisions.

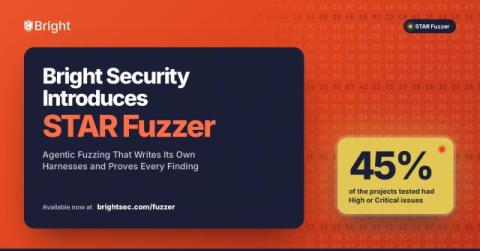
Bright Security Introduces STAR Fuzzer, Agentic Fuzzing That Writes Its Own Harnesses and Proves Every Finding

Built on an evolutionary engine first released in 2018, STAR Fuzzer by Bright Security finds crashes, memory exhaustion and memory-safety bugs in security-critical code without a running application. In its first open source research run, it found High or Critical issues in 45% of the projects tested, and in its first month of availability it produced ten published findings in eight projects, including the Crystal standard library, htop and RIOT OS.

Data Lineage for AI Agents: Takeaways From MIT Technology Review

Security teams built their controls around people, applications, devices, and networks. AI agents operate across all four at once. An agent can pull records from Salesforce, combine them with financial data, summarize the result with a language model, and post it to Slack, with no person touching any step. Each action may look permitted on its own, which means the risk sits in the sequence, and most tools can’t see the sequence.