Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

4 Strategies to Stay Secure in a Connected World

Cybersecurity is a complex term, it’s become all-encompassing and constantly evolving to include new and emerging technologies, attacks, actors, and a myriad of other points. What this means for organizations large, medium, and small is that each must have a cybersecurity plan in place. An interesting point, however, is despite the mindshare cybersecurity now enjoys, the industry itself is still in its relative infancy.
Redline Infostealer Analysis (Part 2)

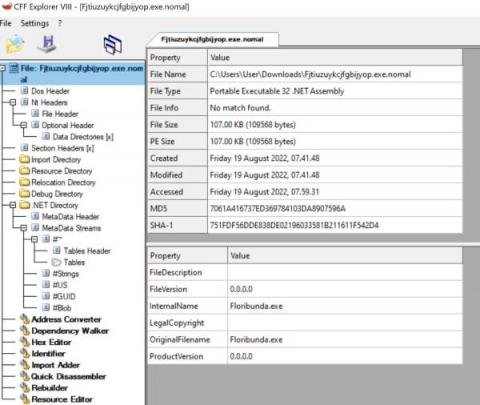
Redline infostealer gathers information and steals high value data from an infected machine. The Redline infostealer is considered one of the most dangerous malware currently being used in the wild and has been used in countless trojanized software, applications, games and cracked software. In addition to data exfiltration, Redline also has the capability to connect to a command and control (C2) server to download, upload files as well as perform remote commands.

Romance fraud losses rose 91% during the pandemic, claims UK's TSB bank

UK banking group TSB is calling on social networks and dating apps to better protect their users from fake profiles, following an alarming spike in romance fraud. Examining data from December 2020 - January 2022, TSB determined that romance fraud almost doubled compared to pre-pandemic levels, with a record increase in losses of 91% - averaging £6,100 per incident.

How Passwords Get Compromised

Have you ever checked on your passwords and noticed a warning that they’ve been compromised? One compromised password can put all your credentials at risk, but how does this happen? Your passwords may be showing as compromised due to a breach, poor password practices or for other reasons. Read on to learn more about compromised passwords and how you can start better securing them.

Software and AppSec Challenges and Opportunities in Banking and Fintech - Part Three

Application security is particularly important in the banking and financial technology sector, where a single breach can put large portions of sensitive information at risk. How to manage that risk is a complex process that affects how teams secure applications across their software supply chain.

Office Hours: Tapping Cloudflare for API Security

This 30-minute interactive discussion was designed specifically for Cloudflare users to learn more about API security challenges and how your existing Cloudflare environment can give you a jumpstart to solve them. Learn how API attacks are different and why industry experts are calling 2023 the year of API security.

5 Advanced DevSecOps Techniques to Try in 2023

If you’re here, you know the basic DevSecOps practices like incorporating proper encryption techniques and embracing the principle of least privilege. You may be entering the realm of advanced DevSecOps maturity, where you function as a highly efficient, collaborative team, with developers embracing secure coding and automated security testing best practices.

Secure your organization with just-in-time access

Just-in-time (JIT) access is a cybersecurity feature where users, applications, or systems are granted access to resources only when needed and for a limited time. This approach limits the risk of privileged accounts gaining unauthorized access to sensitive data. JIT access is often used in conjunction with other security measures—such as multi-factor authentication and encryption—to provide a strong, layered defense against threats.