Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Demo-grade AI vs enterprise-grade AI in GRC tools: What's the difference?

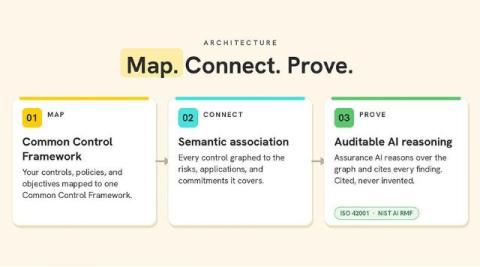
Most GRC platforms claim to use AI. That makes it harder, not easier, to judge the near-identical claims in every demo. Leaders need to know the standards to hold these claims to, what can actually be verified, and how to tell two product pitches apart before letting one of them touch critical controls. It helps to split what you are looking at into two groups: demo-grade AI and enterprise-grade AI. Nearly every GRC vendor now describes itself as the second.

When Agents Trust Each Other, One Compromised MCP Server Is Enough

The agentic AI security conversation has, for good reason, spent most of its energy on the agents an organization builds or deploys directly: what they're authorized to do, what data they can reach, how their behavior is monitored. I think that focus is necessary and also increasingly incomplete, because the fastest-growing risk surface in agentic AI right now isn't the agents themselves.

Yandex outage: Data shows that instead of going dark, malicious bots went on the move

Following reported strikes on Yandex data centers, claims circulated on the Internet that Russian bot farms and influence operations had been knocked offline. HTTP traffic charts showed steep drops, fueling speculation that the infrastructure damage had stopped these malicious actors. However, aggregate traffic metrics can easily mislead. There are two autonomous system numbers (ASNs) associated with Yandex: AS13238 is used by Yandex’s search engine, while AS200350 runs its cloud services.

11 Questions Your Team Should Be Able to Answer This Cybersecurity Awareness Month

A cyberattack is an expensive—and dare I say, inefficient—way to discover whether your cyber resilience strategy works. By the time an executive asks how long it will take to get the business back online, the answer depends on preparation that should already be in place: clearly defined responsibilities, protected data, and a recovery process that someone has actually tested.

Webinar 2026 Cybersecurity Briefing | WatchGuard Webinar

Join WatchGuard CISO Corey Nachreiner and Director of Security Operations Marc Laliberte as they unpack key findings from the WatchGuard Threat Lab’s H1 2026 Internet Security Report. During the lead half of the year, nearly every measure of attack volume fell while nearly every measure of attack variety rose.

How to Find Shadow AI: 3 Hidden Entry Points

For years, companies treated shadow IT primarily as a policy and control problem. Employees have always found and used technology outside the approved IT stack, from unauthorized endpoint applications and browser extensions to personal cloud services. It left a trail: an install, a device on the network, something a scan or an agent could eventually catch. From there, an analyst had to investigate the finding and assess the risk before deciding how to respond.