Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

FedRAMP Without an Agency Sponsor: Program Certification

FedRAMP as a program has been through a lot over the years it has existed. Different authorization paths, different requirements and standards, multiple rounds of streamlining and changes; it's been a rocky road. Things are starting to smooth out now that FedRAMP 20x is broadly available, but there's still a lot to learn or to question before you can be fully up to speed. So, let's talk about authorization and where we stand today.

Acronis Cyber Protect Cloud earns maximum score in AV-TEST Advanced Threat Protection test

Author: Alexander Ivanyuk Advanced attacks often use trusted Windows components and legitimate-looking files to conceal malicious activity. A manipulated DLL can run through a signed executable, while a scheduled task can launch PowerShell to load harmful code. These techniques make independent testing valuable because a security product must recognize the attack chain, not only a suspicious file.

The Year the Vulnerability Backlog Changed Shape

As we enter the AI era, few among us have found themselves so entrenched in the throes of the shifting landscape as CISOs. With the threat landscape shifting, they are up against increasing rates of vulnerabilities and exploits alongside rapidly scaling demands for ever more secure environments. As CISOs, with our role as the protectors of an organization, we are expected to deliver guidance and security visibility. This is not a vision of the future, it’s today’s reality.

Cyber Loss in Rail and Signalling

Cyber risk in transport is usually framed around a collision. Signals manipulated, a train sent onto occupied track, an accident caused deliberately. ‍ Signalling is built to make that outcome unavailable. Any failure forces the system into its most restrictive state, so a compromise produces a halt rather than a crash. The loss is the halt, and rail is unusual in already having a published price for one. ‍

Reading AI Use From the Browser When the Network Sees Nothing

A session to a sanctioned AI provider looks the same on the network whichever account it ran under and whatever was in it. Transport encryption means a proxy sees a connection to an approved domain and a payload size. ‍ Which is fine until somebody asks whether an exposure is reportable. The question turns on three facts the network never held, and none of them can be reconstructed from a log afterward. ‍

Sophos Named a Leader in the IDC MarketScape for Worldwide Modern Endpoint Security for Enterprises 2026

Sophos has been named a Leader in the IDC MarketScape for Worldwide Modern Endpoint Security for Enterprises 2026, recognizing the strength of our prevention-first approach and stopping AI-era threats as early as possible. Attackers using frontier AI models can now find vulnerabilities and generate exploits faster than organizations can patch them. And when malicious code is already running before an alert fires, detection alone is too late.

Key compliance frameworks in Singapore: PDPA, MAS TRM, Cybersecurity Act, and more

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

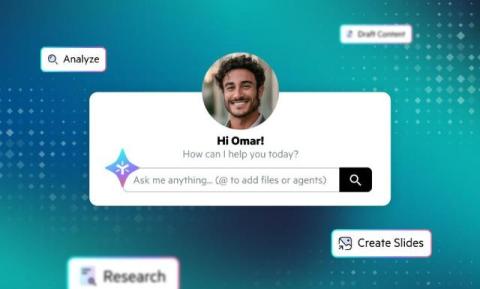
Egnyte's AI Workspace: Where Organizational Knowledge Becomes Action

We've all been there. You're a few minutes from a client call, and you need one clear answer before you jump on. So, you open the project tracker then the shared drive, hunting for the latest email. Then you review a Slack thread to check if that blocker got resolved. By the time you dial in, you've burned fifteen minutes and you're still not fully sure you have the full picture. None of those tools failed you—each one had a piece of what you needed.

The Difference Between Knowing a Vendor Is Risky and Knowing Exactly Which Assets to Fix

When a vendor’s risk score changes, a TPRM team can see what issues were flagged, why they matter, and what remediation steps are recommended next. But improving a vendor’s risk posture is not always as simple as working through each risk finding one by one. Sometimes the bigger pattern sits at the asset level.