Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Security Incident and Event Management.

Automation in Security: Fast Track to Compliance

Manual security operations don't just slow teams down. They make breaches more expensive. Organizations that implement advanced security automation cut breach response time by over 100 days and save an average of $3.05 million per incident, according to JumpCloud's 2024 analysis. That number reframes the conversation. Automation in security isn't a convenience feature for mature SOCs. It's an operating model.

The Definitive SOC 2 Compliance Guide

Every day, service organizations handle sensitive customer information covered by data protection laws and subject to security compliance requirements. In the business-to-business world, customers require that their vendors provide validation and assurance over their privacy and security controls, typically asking for independent third-party attestations and reports.

The New CISO Ep. 147 - Walt Powell | CISO 3.0: The Playbook for Delivering Impact and Influence

What separates a CISO who survives from one who shapes the boardroom? In this episode, Steve Moore sits down with Walt Powell, Lead Field CISO at CDW and author of The CISO 3.0, to unpack the modern CISO playbook—why technical credentials alone no longer cut it, how to build personal eminence, and why most security leaders are still treated as second-class C-suite citizens.

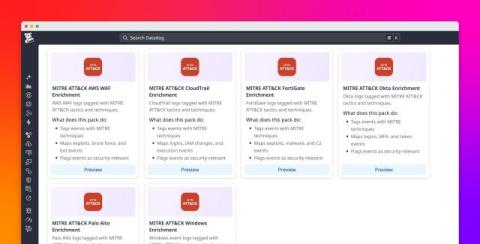
Automatically enrich security logs with MITRE ATT&CK context before they reach your SIEM

To detect and investigate threats, security teams need to collect telemetry data from identity providers, cloud platforms, web application firewalls, and endpoints. But these diverse sources describe the same tactics, techniques, and procedures (TTPs) differently according to their own vendor-specific language. For example, a failed Windows logon appears as an event ID, while an Okta account lockout appears as an identity event.

CMMC Compliance Requirements a Practical Guide for 2026

A lot of defense contractors are in the same spot right now. A solicitation lands, the DFARS language gets stricter, someone asks whether the company is “CMMC ready,” and the room gets quiet because nobody is fully sure what that means in operational terms. Usually, the first instinct is to gather policies, dust off the old SSP, and start checking controls in a spreadsheet. That's not enough anymore. CMMC doesn't reward paper maturity.

Why Short Correlation Windows Miss Insider Risk

Short correlation windows miss insider risk because misuse develops gradually, often over longer periods than detection models track. Short correlation windows miss insider risk because misuse often spans longer periods than detection models track. When context resets at fixed intervals, small behavioral changes fail to accumulate into visible risk. When context resets at fixed intervals, behavior is evaluated in disconnected segments.

ISO 27001 Requirements: A Guide for 2026 Certification

If you're working toward certification, you're probably dealing with the same pattern many organizations encounter. Policies live in shared folders, risk decisions sit in meeting notes, control owners answer questions differently, and audit prep turns into a scramble to prove that security work happened. The hard part usually isn't understanding that ISO 27001 matters. It's translating the standard into repeatable operational evidence.

The World Cup Creates the World's Largest Attack Surface

When 48 teams, 104 matches, 16 host cities, and a broadcast audience approaching half the planet converge across six weeks, something else converges at the same time: opportunity for the people trying to exploit it. The 2026 FIFA World Cup is the most complex digital event in history, and the security challenge it creates is not limited to the tournament organizers.

Network Traffic Analysis: A Guide to Modern Threat Detection

Your team probably already has a SIEM, endpoint telemetry, firewall logs, and a growing backlog of alerts no one wants to tune right before a board update. Then an incident review exposes the same problem security leaders keep finding: the attacker didn't need to defeat every control. They only needed to move through a part of the environment no one was watching closely enough.

Behavior Anomaly Detection: A Practical Guide for 2026

Your SOC probably already has alerts for known bad hashes, suspicious domains, impossible travel, and malware signatures. Then an incident still slips through. The attacker uses valid credentials, touches systems the user can normally access, and moves slowly enough to stay below static thresholds. Nothing looks obviously malicious in isolation. The problem isn't visibility alone. It's that your tools are still asking, “Have I seen this exact pattern before?”