Often, penetration testing (or pen testing) and vulnerability scanning are used interchangeably. In doing so, the importance of each method of testing gets lost in the confusion. Both of these are significant in protecting your data and infrastructure for different reasons. In the age of digitally storing information and companies having an online network presence, it’s easy for hackers to find their way in. This is why both pen testing and vulnerability scanning are important.
You finally have some budget to buy tools for your application security (AppSec) program! GREAT! Purchasing the correct tools for your AppSec pogram can be overwhelming. Even when looking only at point solutions, there still may be some confusion on the value that various tools can provide. Sometimes you'll find the perfect tool, but others may offer you a similar tool with added manual penetration testing (MPT) as part of the overall bundle. That seems like a great idea for the budget.
During a recent client engagement, the DGC penetration testing team identified a previously unknown vulnerability affecting the Autodesk Licensing Service, a software component bundled with nearly all licensed Autodesk products. The vulnerability exists in a software component common to most Autodesk products and impacts nearly all organizations using licensed Autodesk software in any capacity.
Technology has shaped the world magnificently and has become a driving force for businesses and organisations. From academia to big enterprises, everyone is enjoying the perks of technological advancement in the form of applications, IoT devices, online shopping and businesses, portals, etc. including amateur to non-technical people, everyone now utilises some form of a networked-enabled communication system such as email, social media, etc.
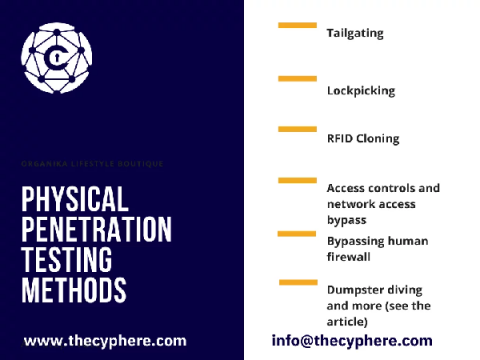
Physical penetration tests are meant to simulate real-world scenarios to help assess the vulnerabilities and risks that could compromise a company’s physical security. Specialists often carry them out in this field who know how to access sensitive information, bypass controls, intercept network traffic and EM waves and more! Physical penetration testing is a vital part of any company’s security.
Trusting the effectiveness of your IT security controls is crucial to mitigate risks and malicious access to your systems and the information they store. Penetration testing with a CREST-Approved provider is one of the most effective methods to gain assurance of your IT security. Initiating a penetration test will give you the ability to develop (or enhance an existing) security strategy and remediate your vulnerabilities.
Penetration testing is a common technique used to analyze the security posture of IT infrastructure. Web application penetration testing can assist you in identifying the potential security weaknesses in your web-based applications so that they can be fixed before attackers exploit them.
Mobile Application Penetration Testing Methodology as a security testing measure, analyses security perimeters within a mobile environment. Derived from the traditional concept of application security methodology, its main focus lies on client-side security and it broadly puts the end-user in control. By conducting penetration testing, companies can gain insights into the source code’s vulnerabilities, bottlenecks, and attack vectors beforehand.