Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Lithic powers the infrastructure behind modern card issuing - S3E13

In this episode, we're excited to introduce Robin Gandhi, Chief Product Officer at Lithic, the programmable card issuing and processing infrastructure for developers, digital banks, and financial institutions handling billions in annual volume. Robin brings over a decade of deep fintech expertise across product, partnerships, and global operations. Before joining Lithic, he served as CPO at Nium, defining payment strategy across 190+ countries, and held leadership roles at Navan (formerly TripActions) and Adyen, where he scaled global issuing and North American partnerships.
Shadow AI - The Hidden Risk in Every Pocket

Shadow AI is already on your employees' phones — and it's invisible to your network controls. This demo follows a real workflow: an employee gets blocked from using an unauthorized AI tool on her corporate laptop, so she switches to her personal phone instead. No VPN, no DLP, no visibility, no corporate controls follow her there.

Let's Talk Security: The Control Gap

In this conversation, Forescout CEO Barry Mainz will be joined by Karsten Abata, tech evangelist at Forescout, former cybersecurity practitioner, and co-author of The Control Gap, to discuss how to close the Control Gap: the widening space between seeing cyber risk and having the ability to control it before it becomes operational impact.

Ep. 67 - The Axis of Disruption: APT41, Volt Typhoon, and the China-Russia Cyber Alliance

For years, Beijing and Moscow kept their cyber tools apart. Not anymore. Hosts Tova Dvorin and Adrian Culley unpack the "no limits" partnership gone operational—the ESA/Galileo satellite attack where a Chinese Volt Typhoon cell opened the door and Russian AcidRain wiper code did the damage. We cover: APT41 running Russian exploit kits, Salt Typhoon pre-positioned in US telecom, China's 72-hour zero-day disclosure law feeding vulnerabilities to Russia, and the CVSS-10 Grimbolt flaw. Why continuous validation and a CTEM program are your best defense against the axis of disruption.

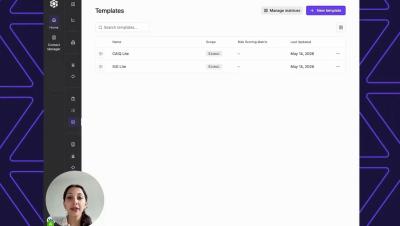
TITAN AI Demo Series: Build Custom Assessment Templates in Minutes with TITAN Agent

Building a strong vendor assessment template used to take hours. With our TITAN Agent, it takes minutes. In this installment of SecurityScorecard's TITAN demo series, see how our TITAN Agent builds customized, comprehensive assessment templates — so your team gets to evaluation faster and with more consistency across every vendor engagement.

The End of the VPN: The Rise of Identity-Based Secure Access

Hundreds of MSPs joined our last webinar to discuss the growing security and operational challenges of remote-user VPNs. Since then, the headlines have only reinforced the problem. Fortinet. Ivanti. Palo Alto Networks. SonicWall. Different vendors, same challenge: critical vulnerabilities, credential theft, and ransomware attacks continue to target remote access infrastructure, forcing organizations into a cycle of emergency patching, user disruption, and increased risk.

Why Project Glasswing Changes the Rules of AppSec

The old application security playbook is broken. With Anthropic’s Claude Mythos and the release of Project Glasswing, AI agents can now autonomously chain low-severity bugs into working zero-day exploits, collapsing the time between vulnerability discovery and active exploitation. In this video, Mend.io's Saoirse Hinksmon (Head of Product Marketing) and Daniel Wyrzykowski (Product Manager) break down the structural shifts in the threat landscape and what security teams must do to keep pace.