Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Intel Chat: Dialogflow Rogue Agent, ghost phishing, CISA KEV deadline & HalluSquatting [338]

Intel Chat with Matt Bromiley and Chris Luft. Matt and Chris break down four stories from the week in threat intel: Stories covered: Chapters: The Cybersecurity Defenders Podcast — a podcast about cybersecurity and the people that keep the internet safe. New episodes drop weekly. Subscribe wherever you listen.

Defence in Depth Changed Forever with Cloud Security

Defence in depth changed forever with cloud security because the old perimeter gave way to platforms, suppliers and connected services outside direct control. That means modern attackers often reach the target through weaker vendors, cloud services or supply chain links instead of attacking the business head on.

How Do You Get Hacked With Zero Malware?

Everyone remembers WannaCry. WantToCry sounds like the same thing. It isn't. It encrypts your files remotely over SMB using nothing but stolen credentials and right now 1.5 million devices are sitting exposed on the public internet. In this episode we break down how remote ransomware works, why your antivirus and EDR never see it coming and what caught it in our Sophos telemetry.

How to manage browser extensions across all clients | ManageEngine MSP Central

Browser extensions are one of the most underestimated security gaps in your clients' environments, and most of them were never approved by your MSP team. In this tutorial, we walk through browser extension management in MSP Central: how to block unauthorized add-ons, restrict dangerous permissions like desktop capture, manage native messaging, and pin approved extensions—all from a single console and enforced automatically across every client.

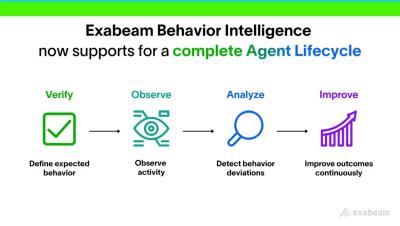
Agentic Trust Controls

As organizations adopt agentic AI, we believe open collaboration is the fastest path to building trustworthy AI governance. Today, we're introducing a new open source project: Agentic Trust Controls. Agentic Trust Controls are designed to help the GRC community evaluate and govern AI agents with greater consistency and confidence. Explore the project and share your feedback at trustcontrols.ai.

How AI Is Accelerating the Cyber Kill Chain?

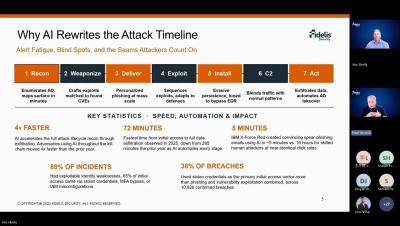
AI Is Accelerating the Cyber Kill Chain: Faster Attacks, Greater Risk AI is changing the speed and scale of modern cyber attacks. From accelerating reconnaissance to reducing the time required for initial access, attackers are leveraging AI to move faster across the entire cyber kill chain. In this video, Paul Girardi explains how AI is impacting each stage of the attack lifecycle, including: As attackers automate more of the kill chain, security teams need smarter approaches to detect, disrupt, and deceive adversaries before they can achieve their objectives.

Can we defend against ai-powered attackers?

In this week's Intel Chat, Chris Luft and Matt Bromiley discuss how the same AI capabilities fueling adversaries are available to defenders too. Matt's takeaway: you don't need to buy an AI product to keep pace. The same way an attacker points AI at a code base, defenders can point it at detection rules and telemetry. Chris adds that as more developers use these models to check their own code, the playing field will level out, though the next year or two will likely bring a spike in exploits from lower-skilled attackers leveraging AI before defenses catch up.